
Cybersecurity researchers specializing in healthcare IoT systems have discovered five serious vulnerabilities that can be exploited to remotely hack Aethon’s TUG autonomous mobile robots.
The TUG robots are used by hundreds of hospitals in North America, Europe and Asia to transport goods, materials and clinical supplies. Their role is to give staff more time to focus on patient care.
However, in order to be able to complete their tasks, the robots require freedom of movement and access to sensitive data, which can make them an attractive target for hackers. Specifically, the robots can access the restricted areas of a healthcare facility, they can operate elevators, open doors, and they have access to patient data.
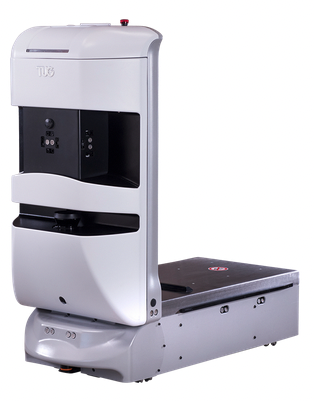 Researchers at healthcare IoT security firm Cynerio have identified a series of critical and high-severity vulnerabilities in these TUG robots — the flaws are collectively named JekyllBot:5 — that could be exploited by threat actors to achieve various goals.
The researchers warned that exploitation does not require special privileges, user interaction or advanced hacking skills, and an attack can even be launched from outside the facility if the robot is accessible from the internet.
The flaws are related to the lack of authorization and identity checks, as well as unsanitized user input. These security weaknesses can allow an unauthenticated attacker to add new admin users to the system, access user credentials, and connect to a control server and hijack the robot.
Cynerio has described several theoretical attack scenarios involving exploitation of the JekyllBot:5 vulnerabilities. An attacker can, for instance, delay the delivery of critical patient medication, or they could even steal medication.
An attacker can also take control of the robot’s movements, making them crash into people or objects.
A hijacked robot can also be used for surveillance through its integrated camera, and the machines can be used to disrupt elevators or doors, which could cause delays in time-sensitive patient care. Another theoretical attack scenario involves accessing protected medical records.
It’s also possible to abuse a robot to deploy malware that can be leveraged for further activities on a compromised facility’s network.
Cynerio notified Aethon about the vulnerabilities before making its findings public, and the vendor has created patches. In addition to releasing firmware updates that address the flaws, Aethon worked with some hospitals in order to help them strengthen their networks and prevent hacking of the robots from the internet.
U.S. cybersecurity agencies have also been notified about the JekyllBot:5 vulnerabilities.
Related: Medical, IoT Devices From Many Manufacturers Affected by ‘Access:7’ Vulnerabilities
Related: Many Healthcare, OT Systems Exposed to Attacks by NUCLEUS:13 Vulnerabilities
Related: CISA Says Philips Vue Healthcare Products Affected by 15 Vulnerabilities






