
Hackers have already started exploiting a recently patched vulnerability affecting F5 Networks’ BIG-IP application delivery controller (ADC).
F5 informed customers last week that a BIG-IP configuration utility named Traffic Management User Interface (TMUI) is impacted by a critical remote code execution vulnerability whose exploitation can result in “complete system compromise.”
The flaw is tracked as CVE-2020-5902 and it was reported to F5 by cybersecurity firm Positive Technologies. The vendor has released patches for impacted versions.
“By exploiting this vulnerability, a remote attacker with access to the BIG-IP configuration utility could, without authorization, perform remote code execution,” explained Mikhail Klyuchnikov, a researcher at Positive Technologies. “The attacker can create or delete files, disable services, intercept information, run arbitrary system commands and Java code, completely compromise the system, and pursue further targets, such as the internal network. RCE in this case results from security flaws in multiple components, such as one that allows directory traversal exploitation.”
Positive Technologies noted that it had identified over 8,000 vulnerable devices that were directly exposed to the internet, but said that most companies did not leave the impacted configuration interface accessible from the web.
Just days after the disclosure of CVE-2020-5902, researchers started releasing proof-of-concept (PoC) exploits for arbitrary file read and remote code execution. Others released scanners that check if a specified BIG-IP installation is vulnerable to attacks and there is even a Metasploit module that helps obtain a root shell.
A video published by DeeLMind shows just how easy it is to exploit the vulnerability if the BIG-IP configuration interface is exposed.
Rich Warren of NCC Group reported on Saturday that the company has already started seeing attempts to exploit CVE-2020-5902. The first attacks observed by NCC read files and extracted encrypted passwords, but they did not attempt remote code execution and the delivery of a binary payload.
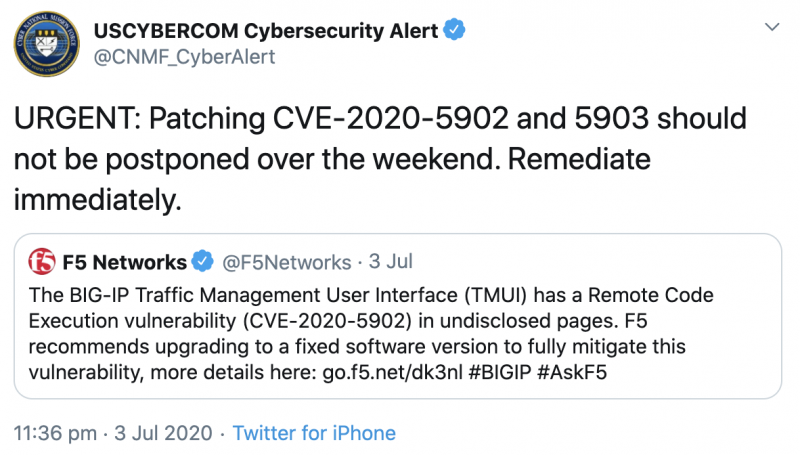
The U.S. Cyber Command has advised organizations to immediately apply the patches for CVE-2020-5902 and CVE-2020-5903, another vulnerability discovered by Positive Technologies that can be exploited to take complete control of a BIG-IP system.
Related: US Cyber Command: Foreign APTs Likely to Exploit New Palo Alto Networks Flaw
Related: Hidden Injection Flaws Found in BIG-IP Load Balancers
Related: “Ticketbleed” Flaw Exposes F5 Appliances to Remote Attacks
Related: Flaw in F5 Products Allows Recovery of Encrypted Data







You must be logged in to post a comment Login