
Researchers say they’ve uncovered a series of potentially serious vulnerabilities in devices made by online privacy firm Winston Privacy. The vendor has released patches that are automatically being sent to devices.
Winston Privacy provides a hardware-based service designed to boost online privacy and security. The company says it can block online surveillance, accelerate browsing, and block ads and trackers, and it also advertises its services as an alternative to traditional VPNs.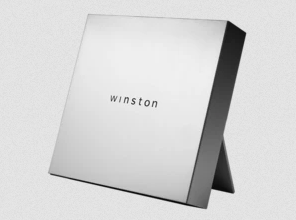
A consultant at offensive security testing company Bishop Fox and an independent researcher discovered a total of 9 vulnerabilities in the device provided by Winston Privacy to customers. Many of the flaws have been assigned a severity rating of critical or high.
The types of security holes identified in the device include command injection, cross-site request forgery (CSRF), improper access control, insecure cross-origin resource sharing (CORS), default credentials, insufficient authorization controls, and undocumented SSH services.
They can be exploited for arbitrary code execution, privilege escalation, changing device settings and launching DoS attacks.
Chris Davis, the Bishop Fox researcher credited for finding the vulnerabilities, told SecurityWeek that an attacker could exploit some of these weaknesses to hack a Winston Privacy device remotely from the internet by convincing the targeted user to access a malicious webpage.
“Alternatively, if an attacker was on the local area network, an unauthenticated API request would also compromise the device,” Davis explained.
Justin Paglierani, the independent researcher credited for finding the vulnerabilities, explained that successful exploitation of the flaws can give an attacker root access to a device.
“In some configurations, this would allow an unauthenticated attacker direct access to your internal network, bypassing NAT, firewalls, etc,” Paglierani said via email. “In other configurations, it would allow an attacker to intercept any unencrypted traffic passing through the device.”
The vulnerabilities were reported to Winston Privacy in July and the vendor told SecurityWeek that it released a critcal hotfix within 24 hours. Patches were then gradually rolled out through last week, when version 1.5.8 was released to patch a remaining minor issue. Firmware updates containing the patches are automatically sent to devices and users do not need to take any action.
“The cost and effort required to mitigate these vulnerabilities was substantial, especially for a small startup,” Richard Stokes, CEO of Winston Privacy, said in an emailed statement. “As a result of these disclosures, we proactively conducted a thorough internal audit of the device and decided that rebuilding and updating the kernel to incorporate leading edge security patches was the best course of action for our users. This led to significant hardening of the device. This underscores the importance of ongoing investment in security which vendors must accept as part of their responsibility to their users. We are proud of the responsiveness we have demonstrated in addressing these issues.”
Bishop Fox has published an advisory with technical details for each of the identified vulnerabilities.
*updated with statement from Winston Privacy and clarifications that the critical vulnerabilities were patched within 24 hours
Related: High Risk Vulnerabilities Addressed in Big Monitoring Fabric
Related: Potentially Serious Vulnerability Found in Popular WYSIWYG Editor TinyMCE







You must be logged in to post a comment Login