The FBI, working in tandem with law enforcement authorities in France, have turned the PlugX malware’s own self-delete mechanism against it, erasing the China-linked remote access trojan from more than 4,200 infected computers in the United States.
Using court-approved access to a command-and-control (C2) server, investigators sent self-delete commands embedded within the malware’s functionality, wiping it clean without disrupting legitimate files or functions.
The FBI operation, conducted alongside French law enforcement and the cybersecurity company Sekoia.io, targeted a version of the malware deployed by Mustang Panda, a hacking group linked to the Chinese government.
The PlugX malware, in circulation since at least 2008, has been publicly documented as a RAT (Remote Access Trojan) used as a backdoor to take full control of infected computers. Once the device is infected, PlugX allows Chinese hackers to harvest data, capture screenshots and keystrokes, reboot the system and manage processes, services and Windows registry entries.
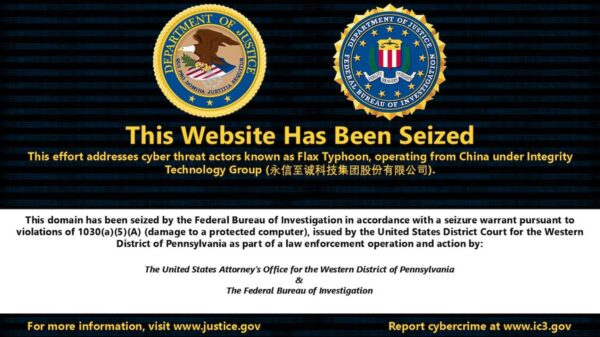
In a published affidavit, the US Justice Department said French authorities gained access to a PlugX command-and-control server and hijacked the malware’s own “self-delete” mechanism to neutralize the threat.
“The international operation was led by French law enforcement and Sekoia.io, a France-based private cybersecurity company, which had identified and reported on the capability to send commands to delete the PlugX version from infected devices,” the agency said in a statement.
“Working with these partners, the FBI tested the commands, confirmed their effectiveness, and determined that they did not otherwise impact the legitimate functions of, or collect content information from, infected computers,” it added.
Notably, the owners of the infected computers had no knowledge of the operation. The FBI said it was working with ISPs to provide notice to US owners of Windows-based computers affected by the court-authorized operation.
“In August 2024, the Justice Department and FBI obtained the first of nine warrants in the Eastern District of Pennsylvania authorizing the deletion of PlugX from US-based computers. The last of these warrants expired on Jan. 3, 2025, thereby concluding the U.S. portions of the operation. In total, this court-authorized operation deleted PlugX malware from approximately 4,258 U.S.-based computers and networks,” the department said.
According to court documents, the Mustang Panda group behind the PlugX malware was paid by the Chinese government to manage cyber operations and develop this specific version of the malware.
“Since at least 2014, Mustang Panda hackers then infiltrated thousands of computer systems in campaigns targeting U.S. victims, as well as European and Asian governments and businesses, and Chinese dissident groups,” the Justice Department said, noting that despite multiple disclosures, owners of computers still infected with PlugX were typically unaware of the infection.
Related: Video Game Firms Targeted With “Paranoid” PlugX Malware
Related: PlugX Malware Adopts New Tactic in India Attack Campaign
Related: PlugX RAT Distributed Via Official Game Installers
Related: PlugX RAT Used to Gather Intel on Afghan, Russian Military