
The financially-motivated hacking group FIN7 has started mailing malicious USB devices to intended victims in an effort to infect their computers with malware, the FBI warns.
Active since at least 2015, the cybercrime group has been focused on stealing credit card information from businesses worldwide. The hackers were indicted in the United States for targeting more than 100 U.S. companies in sectors such as restaurant, gaming, and hospitality.
Mainly targeting businesses via phishing emails, the cybercrime group appears to have changed tactics recently, and started sending malicious USB devices to victims via the United States Postal Service (USPS).
Sometimes, the hackers also included items like teddy bears or gift cards in packages meant for employees in human resources, IT, or executive management roles at the target organizations, the FBI alert reads.
The malicious USB devices are a commercially available tool called “BadUsb Beetle.” They are based on the BadUSB exploit and they can allow attackers to take control of the victim’s machine.
Publicly detailed in 2014 by researchers at Germany-based SRLabs, the BadUSB exploit was meant to demonstrate the threat posed by malicious USB devices. The researchers showed at the time how BadUSB could be used to send commands on behalf of the victim, thus allowing attackers to steal data, install malware, and infect other USB devices.
According to the FBI’s alert, once FIN7’s intended victims plug it into a machine, the USB device starts to automatically inject a series of keystrokes to download and execute the GRIFFON malware, a payload FIN7 often delivers via phishing emails.
“The USB injects a series of keystroke commands, including the (Windows + R) shortcut to launch the Windows Run Dialog to run a PowerShell command to download and execute a malware payload from an attacker-controlled server. The USB device then calls out to domains or IP addresses that are currently located in Russia,” the FBI says.
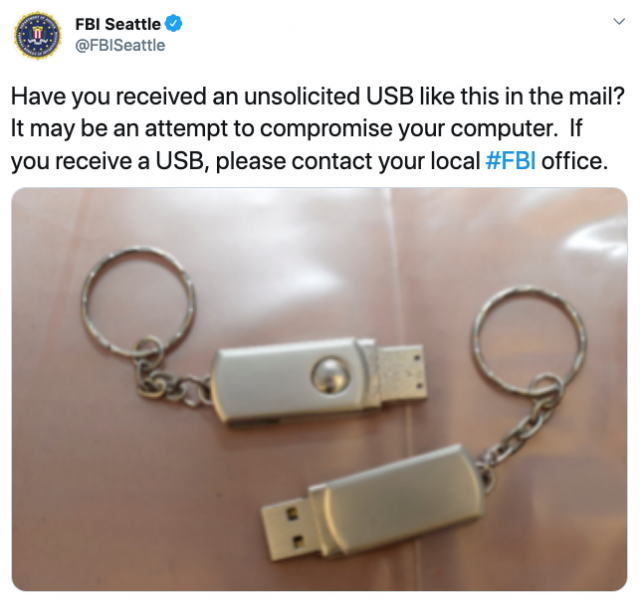
In attacks that Trustwave security researchers observed, fake letters were received alongside the USB drives. Claiming to arrive from Best Buy, which was supposedly giving away $50 gift cards, the letters were encouraging users to plug in the devices to open a list of items they could spend the money on.
Once the device was plugged in, however, the attack would start in the manner described by the FBI.
The malware used in this attack would collect a great deal of system data, including username, hostname, user’s system privileges, operating system information, whether Microsoft Office and Adobe Acrobat are installed, a list of running processes, and whether the host is running in a virtual machine.
Related: USB Device Firmware Can Be Reprogrammed to Hide Sophisticated Malware







You must be logged in to post a comment Login