Dragos says it has found no evidence of a data breach after a known ransomware group claimed to have hacked the industrial cybersecurity company’s systems through a third party.
“Dragos is asked to reach out within 24 hours, or we will begin the publication of both the facts and the data of executive members. This is the result of a third-party breach,” the cybercrime group known as BlackCat and Alphv wrote on its leak website in a post dated November 11.

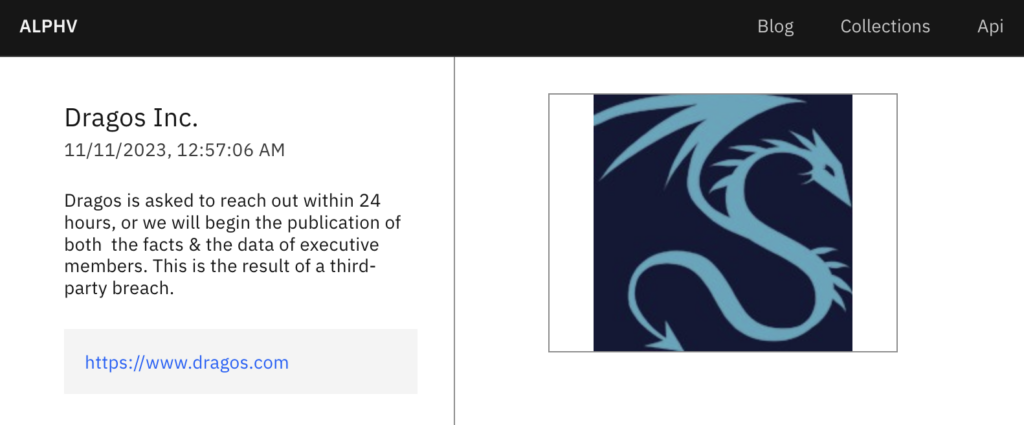
Dragos has launched an investigation, but there is no evidence to date that the hackers’ allegations are true.
“We are aware of an unsubstantiated claim of a breach of information about Dragos executives purportedly from a third-party compromise,” Dragos said in a statement to SecurityWeek. “While security companies like Dragos are often the subject of repeated false claims, we take the responsibility to protect data very seriously and immediately began an investigation into the claims, utilizing our own internal experts and our external security providers.”
“We have not been contacted directly by the criminals and our investigation to date has not produced evidence of a compromise of Dragos systems. We will continue to investigate and monitor this situation,” the company clarified.
This is not the first time a ransomware group has made apparently false claims against Dragos. In October, the threat actor behind the RansomedVC operation, which recently announced closing shop, made contradictory and highly confusing claims about hacking Accenture, Colonial Pipeline and Dragos. At the time, the industrial cybersecurity firm described their claims as “obviously false”.
Dragos did confirm in May that a ransomware group had breached its defenses and accessed threat intelligence reports, a SharePoint portal, and a customer support system.
However, the company said the data breach was limited and an elaborate extortion scheme that included private messages being sent to company executives failed.
Related: ICS Security Firm Dragos Raises $74 Million in Series D Extension
Related: New Dragos OT-CERT Provides Free Industrial Cybersecurity Resources