
Several serious vulnerabilities have been identified in a gateway made by Kunbus, including flaws that can be exploited to take complete control of a device.
Germany-based Kunbus offers connectivity solutions for industrial networks. The company’s gateway products, which are used by various types of organizations around the world, are designed to provide continuous and reliable communications between different networks and systems.
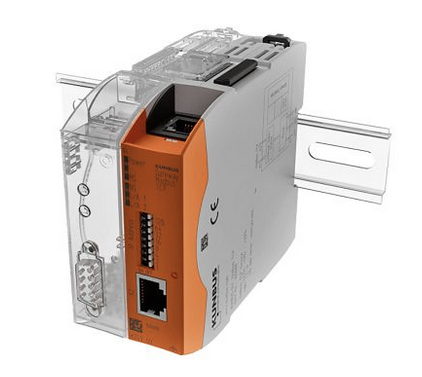 Nicolas Merle, a researcher with industrial cybersecurity firm Applied Risk, discovered that Kunbus’ PR100088 Modbus gateway is affected by a total of five flaws. The issues impact devices running version 1.0.10232 of the software – and likely earlier versions as well – and most of them have been resolved by the vendor with the release of version 1.1.13166 (Security Update R02).
Of the five vulnerabilities, Applied Risk has classified two as “critical” and two as “high severity.”
One of the critical flaws is related to the fact that the gateway’s web application fails to verify that the user is logged in when the password is changed. If an administrator accesses the web interface at some point and the device has not been restarted, an unauthenticated attacker can go to the password changing page and set their own password, even if the legitimate admin is no longer logged in.
The flaw, tracked as CVE-2019-6527, allows malicious actors to take complete control of the device and lock legitimate admins out, Applied Risk says.
Learn More About ICS Flaws at SecurityWeek’s 2019 ICS Cyber Security Conference
Another critical vulnerability, identified as CVE-2019-6533, can be exploited to read and modify the registers used to store Modbus values. This can be done without authentication and it can allow an attacker to cause a denial-of-service (DoS) condition by rebooting the device.
Merle also discovered that when a user authenticates, an HTTP GET request containing their password in clear text is sent to the device. This enables an attacker who can intercept traffic to easily obtain the password.
The researcher also found that an attacker can launch a DoS attack against a device by sending a long request (with a length greater than 256 characters) to the FTP service.
Also related to FTP, the service can be used to retrieve user credentials stored on the device in clear text in an XML file.
The software update released by Kunbus should patch all of these vulnerabilities, except for the last issue, which the vendor expects to fix with Security Update R03 in late February.
In addition to releasing patches, Kunbus recommends that users ensure the devices are used in protected industrial networks, as intended, rather than on public networks.
Advisories describing these vulnerabilities have been published by Applied Risk, ICS-CERT and Kunbus.
Related: Power Grid Protection Firm SEL Patches Severe Software Flaws
Related: Serious Flaws Found in ABB Safety PLC Gateways
Related: Internet Exposure, Flaws Put Industrial Safety Controllers at Risk of Attacks







You must be logged in to post a comment Login