The company will use the investment to accelerate product innovation and expand go-to-market operations.



Hi, what are you looking for?


The company will use the investment to accelerate product innovation and expand go-to-market operations.
The AI security company will invest in product innovation, global expansion, and customer experience.
A crafted prompt to a low-privilege Google ADK agent could be used to pass a malicious hand-off comment to a privileged agent.
Over 24,000 internet-accessible server-management interfaces disclose authentication hashes before login.
An extortion group stole personal, financial, and medical information from the hospital’s network.
The bank holding company was hacked in June, but the investigation into the incident continues.
The physical security firm says its alarm monitoring and system functionality have not been affected.
The INC Ransomware gang has been targeting vulnerable SMA1000 appliances for root access and lateral movement.
Midnight Blizzard has been stealing Microsoft account credentials via compromised Wi-Fi networks at hospitality organizations.
The flaw can be exploited by unauthenticated attackers to read arbitrary files and potentially achieve remote code execution (RCE).
The internet giant has built an agent harness to find vulnerabilities across Chrome’s codebase.
Named CosmosEscape, the vulnerability exposed the primary key for Cosmos DB accounts, granting full read and write access.
In March 2026, hackers stole personal, financial, and medical information from the company’s AWS environment.
Tracked as CVE-2026-63077, the security defect can be exploited without authentication via the agent polling protocol.
The company will accelerate investments in R&D and product innovation to expand its agentic data control plane.
The startup’s community-powered agentic security platform helps proactively identify, prioritize, and remediate vulnerabilities.
The company will invest in accelerating the development and adoption of its agentic platform.
Unauthenticated attackers could send HTTP requests to an exposed endpoint to execute commands inside the MCP bridge container.
Five years after the initial release, the refresh introduces new elements, removes others, and updates terminology.
The major browser update resolves roughly 80 critical- and high-severity security defects.
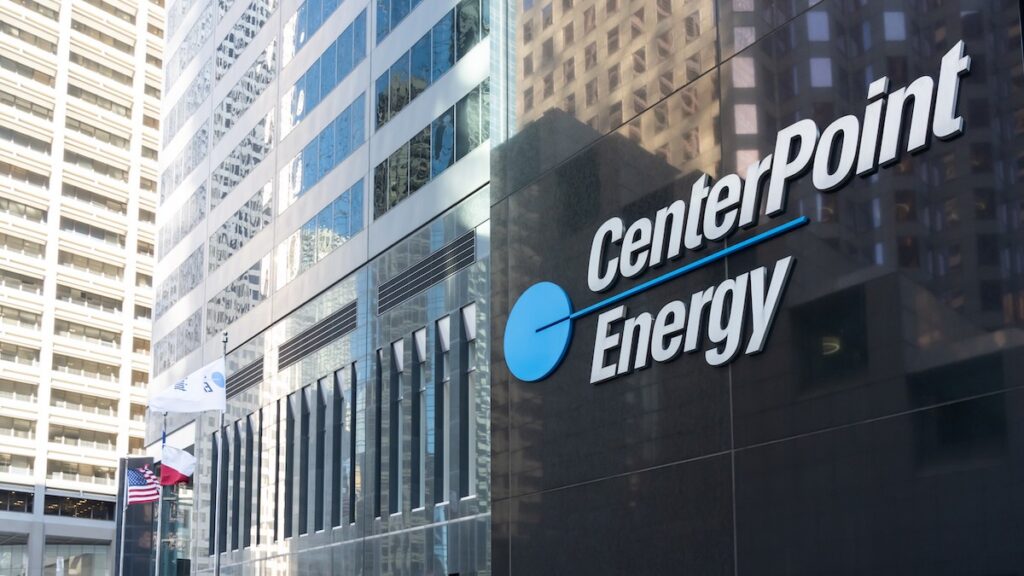
Personal information such as names, addresses, Social Security numbers, and driver’s license numbers was compromised.

Contextual defense helps security teams connect the signals, anticipate what comes next, and stop threats before they escalate.