The Cactus ransomware gang has claimed responsibility for the cyberattack that French industrial giant Schneider Electric disclosed at the end of January.
The incident, the company said at the time, was discovered on January 17 and only impacted its Sustainability Business division, resulting in severed access to Resource Advisor and other systems used by the division.
Schneider Electric has since updated its incident notification to say that it has restored access to the impacted systems and that the attackers exfiltrated certain Sustainability Business data.
Initial reports suggested that the Cactus ransomware group might have orchestrated the attack, and the suspicions have been confirmed, after the gang listed the French giant on its Tor-based leak website.

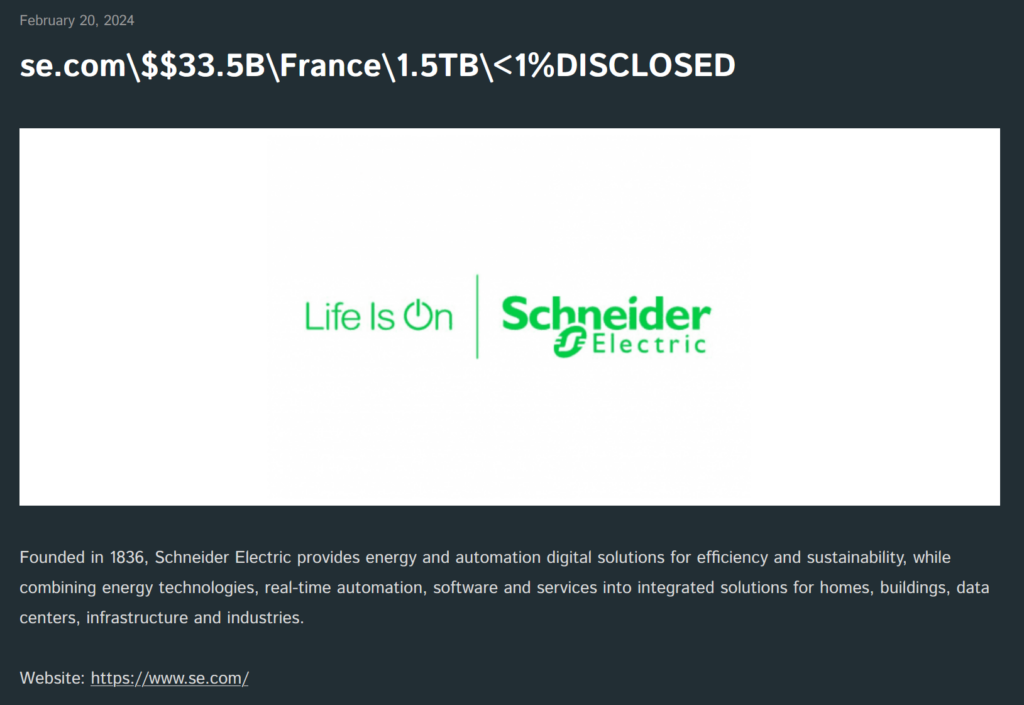
According to Cactus, roughly 1.5 terabytes of data were exfiltrated from Schneider Electric’s systems. The ransomware gang has published a small set of allegedly stolen data, including copies of passports and non-disclosure agreements, and is threatening to make it all public unless a ransom is paid.
Schneider Electric’s Sustainability Business provides sustainability consulting services to large organizations worldwide, including Clorox, DHL, Hilton, and PepsiCo. However, it is unclear how many of these clients were affected by the incident.
Active since at least March 2023, Cactus made headlines in November, when security operations firm Arctic Wolf blamed it for the exploitation of vulnerabilities in a product of business analytics firm Qlik.
It was also observed exploiting Fortinet VPN flaws for initial access, creating an SSH backdoor for persistence, relying on remote access tools, stealing credentials, and encrypting data on all accessible systems.
Cactus has been highly active in the recent months and is currently listing more than 100 companies on its leak site.
Related: Ransomware Group Takes Credit for LoanDepot, Prudential Financial Attacks
Related: US Offers $10 Million for Information on BlackCat Ransomware Leaders
Related: Ransomware Attack Knocks 100 Romanian Hospitals Offline