
Researchers at Trustwave have identified a backdoor in GSM gateways manufactured by Hong Kong-based voice over IP (VoIP) solutions provider DBL Technology.
The company’s DBLTek GoIP devices are designed to bridge GSM and IP networks. DBL Technology has been around for more than 10 years and its products are available worldwide.
In addition to a management web interface, GoIP devices have a telnet-accessible command-line interface. This telnet interface can be accessed using one of two accounts (“ctlcmd” and “limitsh”) protected by a user-set password.
While these accounts can be used to obtain limited information about the device via telnet, experts also discovered an undocumented account, named “dbladm,” which provides root-level shell access to the gateway. The problem is that this account is not protected by a password, but a challenge-response authentication mechanism that can be easily defeated.
When a user attempts to log in to this account, they are presented with a “challenge” number, which they must solve to obtain the password. Trustwave reverse engineered the authentication scheme and determined that there are only five steps to solving it. This includes adding a number to the initial challenge, shifting bits, and generating an MD5 hash.
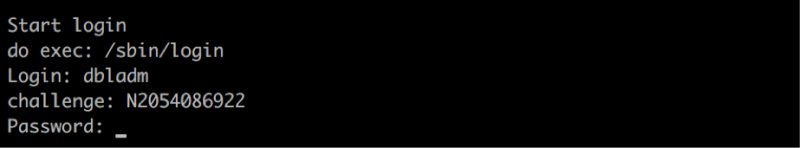
“It is highly likely that this authentication scheme is the result of a testing mechanism built into the ‘/sbin/login’ binary to permit DblTek engineers to login to devices without having to authenticate for devices running on the local network,” Trustwave researchers said.
The backdoor account is present on GoIP devices with 1, 4, 8, 16 and 32 SIM card ports. Experts believe the vulnerability could also affect other products developed by the company.
Trustwave made the first attempt to contact the vendor in October 2016, but it only received a response in December. A firmware update was released on December 21, but experts determined that instead of properly addressing the issue, DBL simply made the challenge more complex.
“It seems DblTek engineers did not understand that the issue is the presence of a flawed challenge response mechanism and not the difficulty of reverse engineering it,” experts said.
SecurityWeek has reached out to DBL Technology for comment and will update this article if the company responds.
Related: Sierra Wireless Rugged Gateways Targeted by Mirai Malware
Related: VoIP Service Servers Abused to Host RATs
Related: VoIP Phone Users Warned About Risks of Default Settings







You must be logged in to post a comment Login