The company will use the funds to expand its sales, partnerships, channels, and customer support teams.


Hi, what are you looking for?


The company will use the funds to expand its sales, partnerships, channels, and customer support teams.
The personalized versions of ChatGPT were used to impersonate legitimate products and trick users into executing PowerShell commands.
Pepijn van der Stap was convicted in 2023 for hacking multiple organizations, stealing their data, and extorting them.
The malware framework uses a modular architecture and a custom executable file format for long-term persistence.
Cameron John Wagenius was sentenced to 70 months in prison for stealing information from the wireless carriers.
The Medicaid IDs and other information of Medicaid and DC Healthcare Alliance beneficiaries were exposed.
The extortion group has modified its exploit in new attacks targeting the PeopleSoft vulnerability CVE-2026-35273.
The company says the measure was precautionary and that it has no evidence of Kiteworks or customer systems being compromised.
The Windows botnet relies on AI to maintain persistence, using xAI Grok to choose from predefined actions.
Ardit Kutleshi created and operated Rydox, which allowed miscreants to trade PII and cybercrime tools and services.
Three vulnerabilities in Salesforce Agentforce allowed hackers to hijack trusted agents, steal data, and launch phishing attacks.
Tracked as CVE-2026-48842, the exploited bug is an SQL injection that can be exploited without authentication.
The startup’s runtime enforcement platform evaluates AI agents in real time to provide visibility and control over their actions.
A threat actor is using three AI harnesses for vulnerability research, exploitation, and attack orchestration.
The vulnerabilities, tracked as CVE-2026-28324 and CVE-2026-28325, can be exploited without authentication.
Hackers impersonated the company’s personnel and contacted its employees to gain access to Astrana Health’s servers.
Tracked as CVE-2026-87902, the path traversal flaw allows remote, unauthenticated attackers to execute arbitrary code.
The nine critical security defects could be exploited for arbitrary code execution and privilege escalation.
The browser update resolves several critical-severity memory safety and memory corruption flaws.
Remote attackers could trigger the critical-severity flaw to access privileged internal functionality.
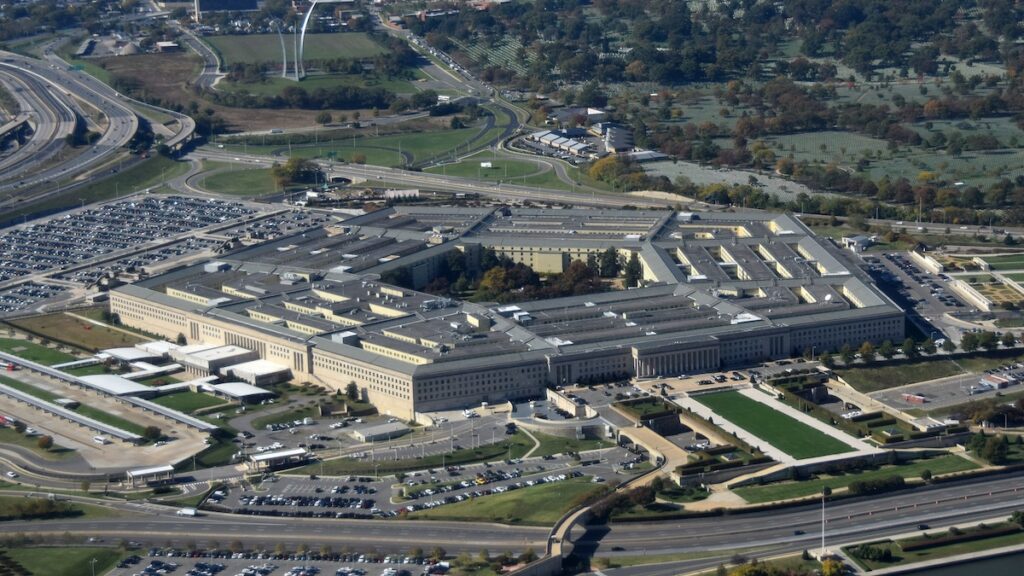

The data breach affects the Defense Manpower Data Center (DMDC), which maintains personnel records for the Department of Defense.


The company will use the funds to expand its sales, partnerships, channels, and customer support teams.