
Software giant Citrix on Friday revealed that its internal network had been breached and the attackers may have stolen business documents.
The company said it was informed by the FBI on March 6 that its systems had been breached by “international cyber criminals.” Citrix has launched a forensic investigation and it has taken action to secure its network.
Citrix’s investigation so far suggests that the attackers may have accessed and downloaded some business documents, but it has yet to determine exactly which documents may have been stolen. The company says there is no evidence that the security of its products or services has been compromised as a result of the attack.
“While not confirmed, the FBI has advised that the hackers likely used a tactic known as password spraying, a technique that exploits weak passwords. Once they gained a foothold with limited access, they worked to circumvent additional layers of security,” stated Citrix CISO Stan Black.
A cybersecurity firm named Resecurity claims the attack was carried out by an Iran-linked group tracked as IRIDIUM, which reportedly hit over 200 organizations, including government agencies, tech firms, and oil and gas companies.
Resecurity said in a blog post it had alerted Citrix of an attack on December 28. The company believes the intrusion resulted in at least 6 terabytes of data getting stolen from Citrix, including emails and files associated with project management and procurement.
“The incident has been identified as a part of a sophisticated cyberespionage campaign supported by nation-state due to strong targeting on government, military-industrial complex, energy companies, financial institutions and large enterprises involved in critical areas of economy,” Resecurity said in a blog post.
“The arsenal of IRIDIUM includes proprietary techniques allowing to bypass 2FA authorization for critical applications and services for further unauthorized access to VPN (Virtual Private Networks) channels and SSO (Single Sign-On),” the firm added.
Resecurity representatives told NBC News that the attackers may have been lurking inside Citrix’s network for the past 10 years.
A recent article from The Wall Street Journal on attacks carried out by Iranian hackers cited Resecurity saying that Citrix had been hit by Iranian hackers. However, in a statement provided to WSJ, the software giant claimed that a single employee account was compromised in 2018 and that the hacker only gained access to an old version of a list containing Citrix employee contact information. Citrix claimed at the time that it had found no evidence that any other accounts had been compromised or that the attack may have been the work of a state-sponsored actor.
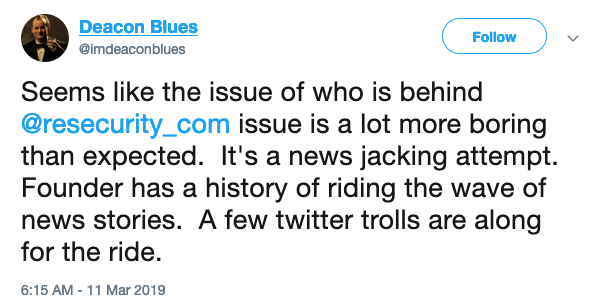
While Citrix has confirmed being hit by a potentially significant breach, cybersecurity experts and others have called into question Resecurity’s claims that Iran was behind the attack.
Resecurity has stated that the recent attack on Australia’s political parties and parliament was also the work of Iranian hackers. The Australian government has not pointed the finger at anyone, but it did say the attack was apparently carried out by a “sophisticated state actor.” However, sources close to the investigation told The Sydney Morning Herald that the prime suspect was actually China.
Kaspersky’s Costin Raiu pointed to some inconsistencies in Resecurity’s claims — the company said the hackers may have had access to Citrix systems for the past ten years, but also told NBC News that Citrix came under attack twice, once in December and “again on Monday” (presumably March 4).
Citrix also suffered a breach back in 2015, but the company claimed at the time that the hacker had not accessed any customer or sensitive corporate data.
Related: OSIsoft Warns Employees, Contractors of Data Breach
Related: HR Software Firm PageUp Finds No Evidence of Data Theft







You must be logged in to post a comment Login