
Android smartphone manufacturers have significantly improved their patching hygiene over the past couple of years, a new report from Security Research Labs reveals.
Starting in 2015, after the Stagefright vulnerability was disclosed, Google has been releasing new security fixes for the Android operating system on a monthly basis, urging vendors to review and integrate those into software updates for their devices.
In 2018, Germany-based Security Research Labs revealed that Android vendors were regularly omitting patches in security updates released to their users, thus leaving them exposed to certain attacks.
Since then, however, the ecosystem has seen improvements in terms of regularly delivered patches, with some vendors releasing fixes to their users much faster than before.
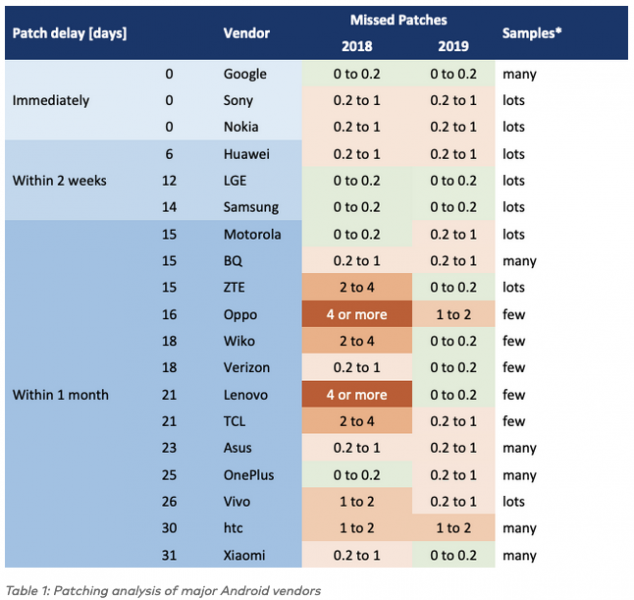
“We found that on average, for official firmwares released in 2019 missed only about half as many patches as comparable firmwares released in 2018,” the security firm says.
Monthly security updates are being integrated into firmware builds 15% faster than in 2018. Last year, 90% of unique firmware builds for major Android vendors arrived within 38 days of Google’s security patches.
Vendors also improved their patching processes, with the rate of missed patches dropping below 0.3 (from 0.7 in 2018).
However, the Android ecosystem continues to become more fragmented: several Android versions are supported at the same time, and unsupported end-of-life versions continue to be widely used.
Only 30% of the observed devices were running Android 9 or newer in 2019, 40% were running Android 8, and 30% were running Android 7.
“Overall, we find that vendors tend to patch their most widely deployed Android versions faster than less-widely deployed versions. Less widely deployed versions, even if more recent, were more likely to see delayed updates or missed patches,” the security firm says.
Vendors such as Nokia and Google deliver patches exceptionally fast, with newer Android versions built days or even weeks before the public Android Security Bulletin is posted, because vendors get access to the information one month in advance.
Those vendors that use vanilla Android on their devices, rather than highly customized versions, deliver patches faster and with less effort. Moreover, they have fewer devices to push patches to, further streamlining the process compared to those which have a large number of devices to maintain.
Over time, most major vendors have made improvements to the patching of new Android versions, with the majority of firmware for supported Android versions being patched recently. Vendors have improved both patching accuracy and speed, the security firm says.
“The remaining patch gap appears arise from the complexity of the ecosystem and the number of Android versions that must be supported by each vendor,” Security Research Labs says.
Related: Google Patches Critical RCE Vulnerabilities in Android’s System Component
Related: Google Patches Critical Remotely Exploitable Android Bug
Related: Android Vendors Regularly Omit Patches in Security Updates






