Cybersecurity research company IOActive has disclosed the details of a new vulnerability impacting AMD processors, but the chip giant pointed out that the weakness is not easy to exploit.
The vulnerability, dubbed Sinkclose and tracked as CVE-2023-31315, targets System Management Mode (SMM), a high-privilege operating mode in x86 processors used for low-level system management functions.
IOActive described it in a talk at the DEF CON conference over the weekend as one of the most powerful execution modes, providing full access to system and I/O device memory. SMM is not visible to the OS and hypervisors.
According to IOActive, the Sinkclose vulnerability, which has been around for nearly two decades, can allow an attacker to gain deep access to a targeted system. The company’s researchers pointed out that a Sinkclose attack, which is possible due to a CPU design flaw, can allow threat actors to break secure boot and in some cases even to deploy firmware implants.
The researchers admitted that exploitation of the flaw requires in-depth understanding of the targeted architecture, but noted that exploitation does not require physical access to the system. They plan on releasing exploit code in a few weeks.
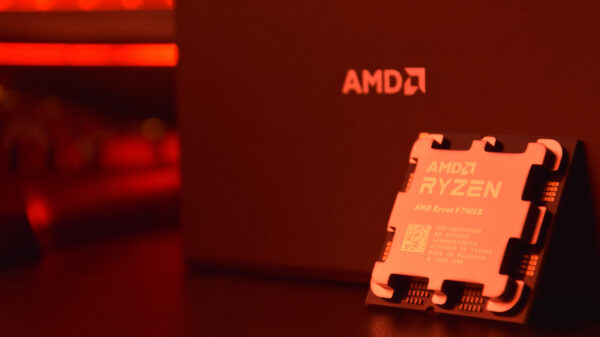
They noted that most AMD CPUs are impacted, including Ryzen and Epyc series processors, which means hundreds of millions of devices may be exposed to Sinkclose attacks.
In response to the research, AMD has published a security advisory with mitigations for Sinkclose attacks. The company has also started releasing firmware updates and plans on releasing more in the upcoming period, but some older CPUs will not receive patches.
“Improper validation in a model specific register (MSR) could allow a malicious program with ring0 access to modify SMM configuration while SMI lock is enabled, potentially leading to arbitrary code execution,” AMD wrote in its advisory.
AMD has thanked IOActive for responsibly disclosing the vulnerability and working with its product security team to address the issue.
“While the issue only affects seriously breached systems, AMD prioritizes security. We believe our mitigations available today are an appropriate response to the threat,” AMD told SecurityWeek in an emailed statement.
“AMD has released mitigation options for its AMD EPYC™ datacenter products and AMD Ryzen™ PC products,” it added.
When it says that the issue only impacts “seriously breached systems”, AMD is referring to the fact that an attacker needs to leverage other vulnerabilities to defeat the operating system’s security measures and gain kernel privileges before exploiting Sinkclose.
While this may be achievable for sophisticated threat groups, such as state-sponsored actors, by the time they obtain the privileges required to conduct an attack, they already have complete control of the system, being able to steal sensitive data, disable security features, and cause disruption.
The malware that can be planted using the Sinkclose method would be stealthy, but not impossible to detect.
Related: ZenHammer Attack Targets DRAM on Systems With AMD CPUs
Related: Chipmaker Patch Tuesday: Intel, AMD Address New Microarchitectural Vulnerabilities