
Connect with us

Hi, what are you looking for?

SecurityWeekSecurityWeek

Cloud Security

$320,000 Paid Out at Zeroday.Cloud for Open Source Software Exploits

Participants earned rewards at the hacking competition for Grafana, Linux Kernel, Redis, MariaDB, and PostgreSQL vulnerabilities.

Zeroday.Cloud competition

Researchers earned a total of $320,000 at the Zeroday.Cloud live hacking competition organized this week in London by cloud security giant Wiz.

Wiz teamed up with AWS, Google Cloud, and Microsoft for Zeroday.Cloud, which had a total prize pool of $4.5 million for vulnerabilities in core cloud and AI technologies.

Participants were invited to demonstrate exploits across six categories, including AI, Kubernetes and cloud native, containers and virtualization, web server, DevOps and automation, and database. Rewards ranging between $10,000 and $300,000 have been offered.

The white hat hackers who took part in the event earned a total of $320,000 for 11 exploits targeting various open source technologies.

On the first day of Zeroday.Cloud, researchers were awarded a total of $200,000. The biggest single payout was $40,000 for a Linux kernel exploit.
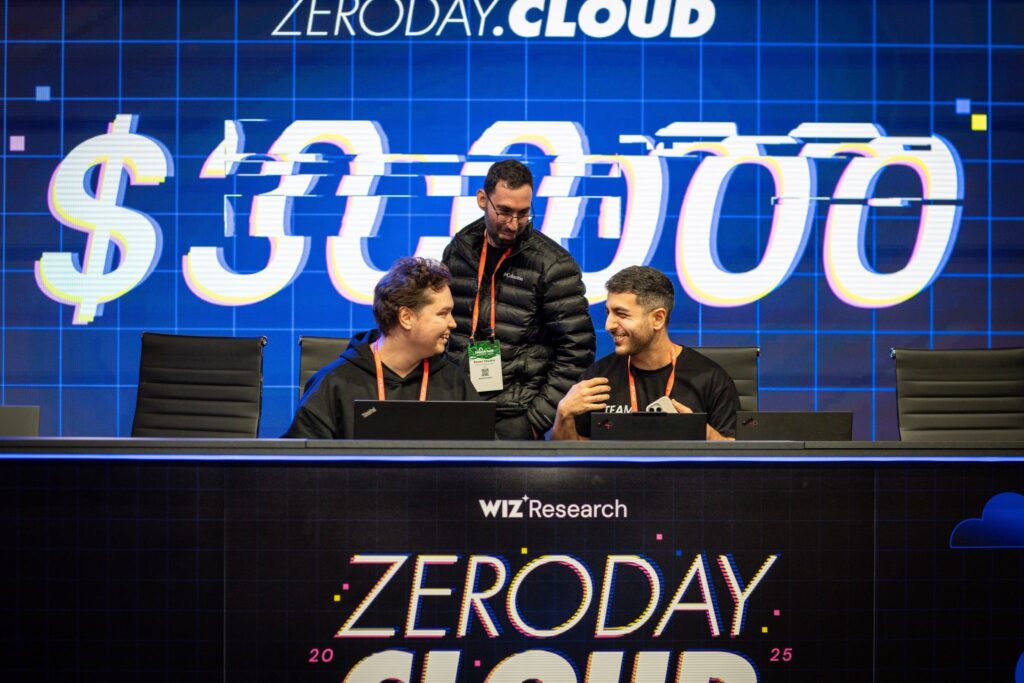
Researchers earned $30,000 each for five database system exploits: three targeting Redis and two aimed at PostgreSQL. 

An authenticated remote code execution exploit targeting the Grafana observability platform earned a team $10,000.

Advertisement. Scroll to continue reading.

On the second day, participants earned a total of $120,000. Three different targets were successfully compromised for $30,000 each: PostgreSQL, MariaDB, and Redis. Redis was exploited a second time, bringing its total reward for the day to $60,000.

Researchers also attempted to demonstrate exploits for the vLLM and Ollama LLM tools, but their attempts were unsuccessful within the allotted timeframe.

Related: Trump Signs Executive Order to Block State AI Regulations

Related: Google Patches Gemini Enterprise Vulnerability Exposing Corporate Data

Related: Google Fortifies Chrome Agentic AI Against Indirect Prompt Injection Attacks

Related: Vulnerability in OpenAI Coding Agent Could Facilitate Attacks on Developers

Written By

Eduard Kovacs (@EduardKovacs) is senior managing editor at SecurityWeek. He worked as a high school IT teacher before starting a career in journalism in 2011. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing for the latest cybersecurity threats, trends, and expert insights.

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

AI tools connected to Google Workspace can access millions of sensitive emails and files. Join this session to uncover your organization’s risk and learn a framework to manage AI access.

Register

Join as we bring together CISOs, senior cybersecurity executives, practitioners, industry experts, and other security leaders to share practical experience and examine the issues shaping enterprise cybersecurity strategy.

Register

People on the Move

Noma Security has named Bobby Shoker as CFO and Alberto Rodrigues as CCO.

Neo has appointed Scott Stout as CRO.

CISA has sworn in Kan Wang as CFO and Khoi Nguyen as CAE.

More People On The Move

Expert Insights

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest cybersecurity news, threats, and expert insights. Unsubscribe at any time.





