
Air Force officials revealed more details about a malware infection that impacted systems at the Creech Air Force Base in Nevada.
The malware attack received media attention last week when Wired.com reported malware had infected the cockpits of fighter drones used by the Air Force. Citing sources on the base, Wired reported that the malware was first discovered in September and had resisted attempts to clean computer systems.
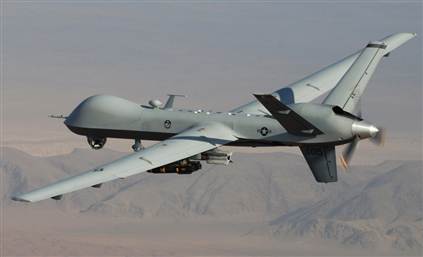 According to the Air Force, the 24th Air Force (24th AF) first detected the malware – which they characterized as a “credential stealer” as opposed to a keylogger as originally reported – and notified Creech Air Force Base officials Sept. 15 that malware was found on portable hard drives approved for transferring information between systems.
The infected computers were part of the ground control system that supports remotely-piloted aircraft (RPA) operations. The malware is not designed to transmit data or video or corrupt any files, programs or data, according to the Air Force, which explained the infected computers were part of the ground control system that supports drone flight operations. The ground system is separate from the flight control system used by RPA pilots to fly the aircrafts.
Related Reading: The Veterans of the Future will be Those in Computer-Based Combat
Military drones have played a significant role in the War on Terror and operations associated with the wars in Afghanistan and Iraq. Due to the classified nature of the drone program, military officials had been relatively tight lipped about the incident during the past several days. However, Col. Kathleen Cook, spokesperson for Air Force Space Command, said it was important to “declassify portions of the information associated with this event to ensure the public understands that the detected and quarantined virus posed no threat to our operational mission and that control of our remotely piloted aircraft was never in question.”
In comments to the Associated Press, one defense official reportedly characterized the malware as the type used to steal log-in and password information for online games such as Mafia Wars.
“We continue to strengthen our cyber defenses, using the latest anti-virus software and other methods to protect Air Force resources and assure our ability to execute Air Force missions,” Cook said in a statement. “Continued education and training of all users will also help reduce the threat of malware to Department of Defense systems.”
Related Reading: Guerilla Cyber Warfare: Are We Thinking Defensively?
Related Reading: Code Wars: The Cold War Gone Tech
Related Reading: iPhone App Helps Train U.S. Army Patriot Missile Crews
Related Reading: ‘Network in Box’ Brings Connectivity to Warfighters at the Edge of the Battlefield







You must be logged in to post a comment Login