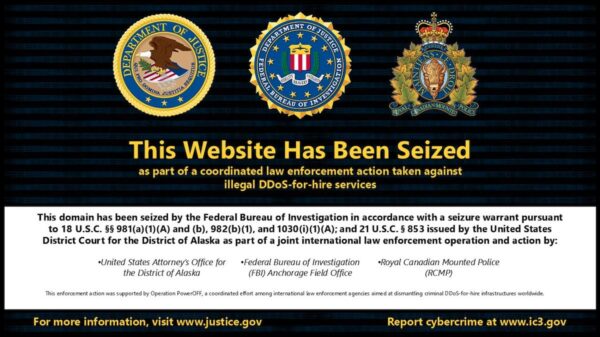
US authorities this week announced the takedown of E-Note, a cryptocurrency exchange allegedly involved in laundering money for ransomware groups and other cybercriminal organizations.
E-Note, the US says, has been used to transfer over $70 million in illicit funds since 2017, including proceeds from cyberattacks against healthcare and critical infrastructure entities in the United States.
According to the authorities, the E-Note payment service and money mule network were used to transfer proceeds originating from ransomware attacks and account takeover incidents.
In conjunction with the E-Note takedown, the US announced charges against Mykhalio Petrovich Chudnovets, 39, of Russia, who controlled and operated the crypto exchange.
According to the indictment, Chudnovets has been offering money laundering services since 2010.
Court documents allege that Chudnovets used the E-Note payment processing services to transfer illicit proceeds for financially motivated cybercriminals.
The funds were sent across international borders and converted to various cash currencies, the documents show.
The US authorities seized servers hosting Chudnovets’s infrastructure, mobile apps, and the domains ‘e-note.com’, ‘e-note.ws’, and ‘jabb.mn’.
US law enforcement also obtained earlier copies of the servers, including customer databases and transaction records, the Department of Justice announced.
Chudnovets was charged with money laundering conspiracy and faces up to 20 years in prison.
Related: $29 Million Worth of Bitcoin Seized in Cryptomixer Takedown
Related: Ukrainian Man Extradited From Ireland to US Over Conti Ransomware Charges
Related: 1,000+ Servers Hit in Law Enforcement Takedown of Rhadamanthys, VenomRAT, Elysium
Related: German Authorities Take Down Crypto Swapping Service eXch