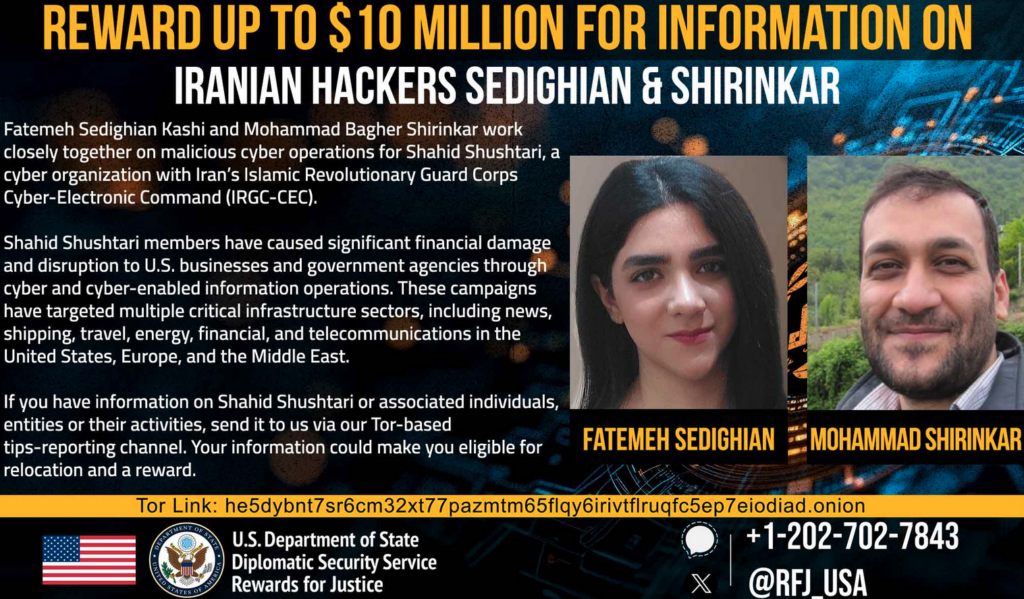
The US government has announced rewards of up to $10 million for information on members of the Iranian hacking group known as Emennet Pasargad.
The reward offers come roughly a year after a US-Israel joint advisory described the activities of the group, which was then identified by the name of its front company, Aria Sepehr Ayandehsazan (ASA).
Noting that the group was previously identified as Emennet Pasargad, Ayandeh Sazan Sepehr Arya (ASSA), Eeleyanet Gostar, and Net Peygard Samavat Company, the US now calls it Shahid Shushtari.
In the private sector, the threat group has been known as Cotton Sandstorm, Marnanbridge, and Haywire Kitten.
According to the US, which has been tracking the activities of the group since 2020, Shahid Shushtari is an organization operating under Iran’s Islamic Revolutionary Guard Corps Cyber-Electronic Command (IRGC-CEC).

Last year, the group was blamed for attacks against the 2024 Summer Olympics and the systems of a US-based IPTV streaming company, and was previously sanctioned for influence operations targeting the 2020 presidential election.
Now, the US has named Mohammad Bagher Shirinkar as the leader of Shahid Shushtari, and Fatemeh Sedighian Kashi as a long-time employee of the front company.
“Sedighian and Shirinkar maintain a close relationship, and Sedighian works closely with Shirinkar in the planning and conduct of cyber operations,” the US says.
According to the US, the hackers are operating out of Tehran, conducting cyberattacks and influence operations against critical infrastructure sectors in the US, Europe, and the Middle East, including news, shipping, travel, energy, financial, and telecommunications organizations.
“Anyone with information on Mohammad Bagher Shirinkar, Fatemeh Sedighian Kashi, Shahid Shushtari or associated entities and/or individuals linked to malicious cyber activities targeting U.S. critical infrastructure or foreign interference in U.S. elections should contact Rewards for Justice via our Tor-based tips-reporting channel,” the US notes.
Related: Amazon Details Iran’s Cyber-Enabled Kinetic Attacks Linking Digital Spying to Physical Strikes
Related: Iranian Hackers Target Defense and Government Officials in Ongoing Campaign
Related: In Other News: Iranian Ships Hacked, Verified Android Developers, AI Used in Attacks
Related: Iranian APT Targets Android Users With New Variants of DCHSpy Spyware