Europol, Microsoft, and cybersecurity companies on Wednesday announced a joint effort to take down the widely used phishing-as-a-service platform Tycoon 2FA.
Tycoon 2FA is a subscription-based platform that enables threat actors to impersonate users, create phishing pages, and bypass multi-factor authentication (MFA). It has allowed malicious hackers to intercept authentication sessions and gain access to targeted email and cloud accounts without triggering alerts.
“Tycoon 2FA combined convincing phishing templates, realistic landing pages, and real‑time capture of credentials and authentication codes into an easy‑to‑use package that scaled quickly. By lowering the technical barrier to entry, it allowed criminals with limited expertise to run sophisticated impersonation campaigns,” Microsoft said.
According to the tech giant, Tycoon 2FA accounted for roughly 62% of the phishing attempts it blocked last year. The platform had been used to send out tens of millions of phishing emails to 500,000 organizations every month.
“Despite extensive defenses, the service is linked to an estimated 96,000 distinct phishing victims worldwide since 2023, including more than 55,000 Microsoft customers,” Microsoft said.
The disruption of the cybercrime platform involved court orders, intelligence from major cybersecurity firms, and the seizure of 330 active Tycoon 2FA domains, including control panels and phishing pages.
Law enforcement agencies in Latvia, Lithuania, Portugal, Poland, Spain, and the UK were involved in disrupting Tycoon 2FA, Europol said.
The list of security companies that also participated in the operation includes Cloudflare, Proofpoint, Intel471, TrendAI, Resecurity, SpyCloud, and eSentire, along with the cryptocurrency exchange Coinbase, the law firm Crowell, and cybersecurity organizations Shadowserver and Health-ISAC.

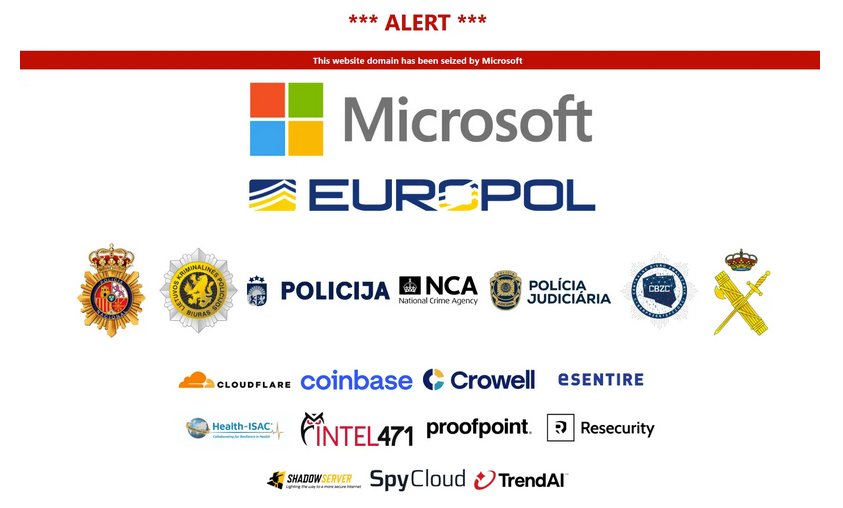
In addition to the takedown of the Tycoon 2FA infrastructure, legal action has been taken against multiple individuals suspected of running the operation, including Saad Fridi, based in Pakistan and believed to be the platform’s main developer.
Related: RaccoonO365 Phishing Service Disrupted, Leader Identified
Related: SystemBC Infects 10,000 Devices After Defying Law Enforcement Takedown
Related: 1,000+ Servers Hit in Law Enforcement Takedown of Rhadamanthys, VenomRAT, Elysium