
Government
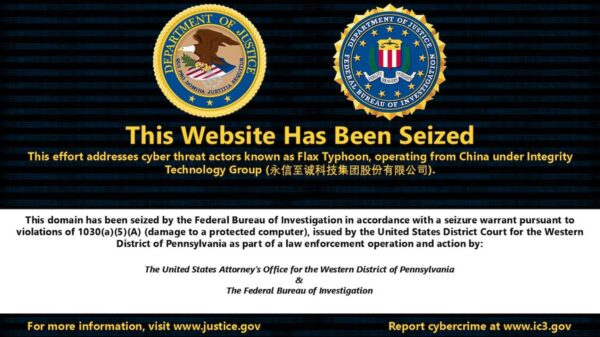
Flax Typhoon and other APTs used MicroScan and FishHub to scan and hack US and foreign critical infrastructure.
Hi, what are you looking for?

Flax Typhoon and other APTs used MicroScan and FishHub to scan and hack US and foreign critical infrastructure.
The Chinese-language input method editor for Windows can allow attackers to execute arbitrary code remotely.
The operation focused on a group named QTFY, which offers hacking services to the Chinese government and others.
Chinese cybersecurity firms are facing action from the country’s military, but it’s not due to product or technical failures.

Google’s Threat Intelligence Group has been tracking the cyberespionage group as UNC6508 since early 2025.
Salt Typhoon has hit an energy entity in Azerbaijan. Twill Typhoon has targeted Asian entities with an updated RAT.
The cybersecurity firm has not explicitly accused China of being behind the attack, but the evidence suggests it was.
Dubbed GopherWhisper, the group relies on multiple Go-based backdoors alongside custom loaders and injectors.
The state-sponsored threat actor deployed kernel implants and passive backdoors enabling long-term, high-level espionage.
The state-sponsored hackers deployed custom tools and stayed dormant in the compromised environments for months.
The UNC2814 threat actor has been active since at least 2017, targeting organizations across 42 countries.
The vulnerability in TeamT5 ThreatSonar Anti-Ransomware was recently added to CISA’s KEV catalog.
GTIG and Mandiant said the zero-day tracked as CVE-2026-22769 has been exploited by UNC6201 since at least 2024.

China-linked UNC3886 targeted all four major telecom providers, but did not disrupt services or access customer information.
Palo Alto Networks has not attributed the APT activity to any specific country, but evidence points to China.
The threat actor uses a signed driver file containing two user-mode shellcodes to execute its ToneShell backdoor.
The British government is investigating a “cyber incident” following news reports that hackers linked to China have gained access to thousands of confidential documents.
The hacking group has been using Group Policy to deploy cyberespionage tools on governmental networks.
The critical zero-day is tracked as CVE-2025-20393 and it impacts Secure Email Gateway and Secure Email and Web Manager appliances.
Google has also mentioned seeing React2Shell attacks conducted by Iranian threat actors.
The suspect is believed to be Edward Dubrovsky, a Canadian cybersecurity executive who was visiting the United States for a conference.



The all-stock deal brings Elisity’s least-privilege access technology into IonQ’s security portfolio.