Artificial Intelligence
Emerging from stealth with $16 million in pre-seed funding, Outerlimit offers a decentralized authorization layer designed to discover, observe, and block harmful autonomous AI...
Hi, what are you looking for?

Emerging from stealth with $16 million in pre-seed funding, Outerlimit offers a decentralized authorization layer designed to discover, observe, and block harmful autonomous AI...
Attack demonstrates how LLM agents can combine known exploitation techniques with real-time reasoning to automate complex, multi-stage intrusions.
Context is the central plank of AI in general, and agentic AI in particular. If an AI system doesn’t have the correct context, it...
The AI Risk Quadrant evaluates AI agents based on three factors: how vulnerable they are to compromise, the potential impact of a breach, and...
CISOs are now facing machine-speed attacks and asking, “How do I agent?” The industry must provide remediation at scale.
From autonomous code generation to decision-making systems that initiate actions without human intervention, the industry is entering a new phase.
When software can think and act on its own, security strategies must shift from static policy enforcement to real-time behavioral governance.
Without proper security controls, AI agents could perform malicious actions, such as data exfiltration and malware installation.
The cybersecurity company has launched Digital Security Teammate (DST), AI agents that investigate, triage, and escalate incidents when needed.

A state-sponsored threat actor manipulated Claude Code to execute cyberattacks on roughly 30 organizations worldwide.
Agentic AI speeds operations, but requires clear goals, least privilege, auditability, red‑teaming, and human oversight to manage opacity, misalignment, and misuse.
The company’s IAM platform identifies AI agents, supports assigning permission to them, and tracks all activity.
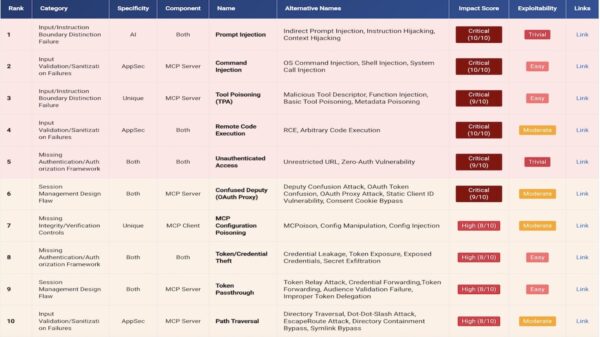

A new ranking of Model Context Protocol weaknesses highlights critical risks—from prompt injection to command injection—and provides a roadmap for securing the foundations of...
Geordie has developed a platform that gives enterprises deep visibility into AI agents and what they are doing.
From prompt injection to emergent behavior, today’s curious AI models are quietly breaching trust boundaries.


Experts unpack the risks of trusting agentic AI, arguing that fallibility, hype, and a lack of transparency demand caution—before automation outpaces our understanding.
As organizations rush to adopt agentic AI, security leaders must confront the growing risk of invisible threats and new attack vectors.
Maze and its investors are betting on finding profits in software that uses AI-powered agents to automate critical parts of the process.
Agentic AI can be a great tool for many of the ‘gray area’ tasks that SOC analysts undertake.


Athena marks a major leap in SOC automation, enabling real-time detection, triage, and remediation with minimal human oversight.
Researchers show that file-change notification systems can leak keystroke timing, browsing activity, and WhatsApp media events.
Noteworthy stories that might have slipped under the radar: BragJack attack against browser AI assistants, TDengine flaw threatens industrial telemetry uptime, Ubuntu update overhaul.