Vulnerabilities
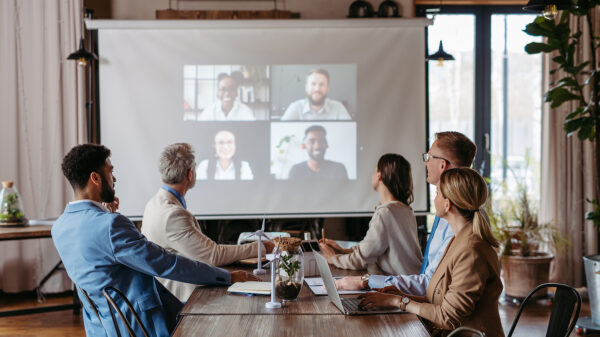
CISA has removed from its KEV catalog five Owl Labs video conferencing flaws that require the attacker to be in Bluetooth range.
Hi, what are you looking for?

CISA has removed from its KEV catalog five Owl Labs video conferencing flaws that require the attacker to be in Bluetooth range.
CISA says Known Exploited Vulnerabilities Catalog has helped federal agencies significantly accelerate their vulnerability remediation pace.
VWware patches critical flaws that allow hackers to bypass SSH authentication and gain access to the Aria Operations for Networks command line interface.
The FBI is investigating an apparent hack of a national law enforcement database that it maintains.