Several potentially serious vulnerabilities have been discovered in some of the industrial 4G routers made by Phoenix Contact, a Germany-based provider of industrial automation, connectivity and interface solutions.
The security holes were discovered by cybersecurity consultancy SEC Consult and the vendor has released firmware updates that should patch the flaws.
The vulnerabilities affect various Phoenix Contact TC ROUTER and TC CLOUD CLIENT devices. TC ROUTER is a line of industrial 3G/4G routers designed for scenarios where a wired internet connection is not available. TC CLOUD CLIENT devices provide an industrial VPN gateway for remote maintenance via a 4G network.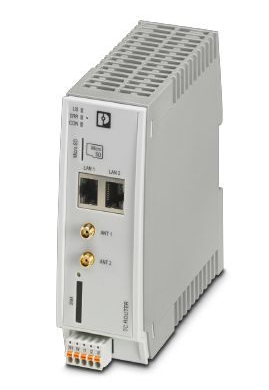

SEC Consult has discovered three types of vulnerabilities affecting these routers. One of them, classified as critical and tracked as CVE-2020-9435, is related to the existence of a hardcoded certificate used for HTTPS. An attacker can leverage this certificate for man-in-the-middle (MitM) attacks, device impersonation, and passive decryption, allowing them to obtain administrator credentials and other sensitive information. The company told SecurityWeek that traffic can be intercepted by an attacker who is in proximity of the targeted router.
The Censys internet search engine shows that there are more than 200 internet-exposed devices using this certificate.
Germany’s VDE CERT says the pre-installed certificates should be replaced by users during the device’s initial configuration. The organization has provided instructions for carrying out this task and says the vendor will ship devices with individual certificates in the future.
Learn More About Flaws in Industrial Products at SecurityWeek’s 2020 ICS Cyber Security Conference
Another vulnerability, tracked as CVE-2020-9436 and rated high severity, can be exploited by an authenticated attacker for command injection, allowing them to compromise the device’s operating system.
The last vulnerability is related to the use of an outdated and vulnerable version of the BusyBox toolkit. The version used in these devices is affected by several vulnerabilities, including ones that could be used for code execution and writing arbitrary files.
While exploitation of these weaknesses requires authentication, SEC Consult told SecurityWeek that an attacker could use default credentials — if they have not been changed — and possibly even cross-site request forgery (CSRF) attacks to obtain the access required for exploitation.
“The impact can be severe for companies using such devices because these kind of SCADA/RTU devices are often used for critical infrastructure,” Johannes Greil, head of the SEC Consult Vulnerability Lab, said via email.
The vulnerabilities were reported to the vendor in late January and firmware updates were released in early March, which is impressive for an industrial solutions vendor. It often takes organizations many months to patch vulnerabilities reported by external researchers.
However, Phoenix Contact does not have a clean record either. Last year, it took the company several months to release an advisory for some serious vulnerabilities that had been publicly disclosed by a researcher. The flaws could have been exploited to hack PLCs directly from the internet.
Related: Flaws Expose Phoenix Contact Industrial Switches to Attacks
Related: Flaws in Phoenix Contact Automationworx Allow Code Execution via Malicious Files
Related: Critical Flaws Patched in Phoenix Contact Industrial Switches