Europol says a 16-year-old is believed to be the administrator and main operator of KillSec, a ransomware group linked to roughly 1,000 suspected attacks worldwide.
The teen was identified in Operation KillSwitch, an international investigation led by police and prosecutors in Germany. Authorities made three provisional arrests and searched eight homes in Greece, Romania, Spain, and the UK.
Investigators also identified a suspected developer who turned 18 in August, as well as one suspected negotiator and one suspected affiliate. The hunt for other possible members continues.
On Wednesday, police took over KillSec’s dark web leak site and blocked further unauthorized access to at least 110TB of data, presumably stolen from victims. Europol said the group used the site to threaten organizations with publishing stolen files unless they paid a ransom. Victims who refused could see their files offered as free downloads.
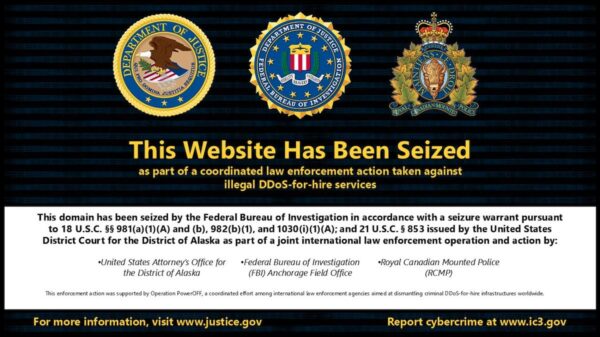
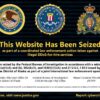
Over the course of the investigation, police also gained control of five core servers, including systems the gang used to manage its operations and hold data stolen from victims. KillSec’s domains now redirect visitors to a law enforcement seizure notice.
KillSec, active since around 2024, broke into organizations through software flaws and weakly protected entry points, especially into cloud storage. It then copied sensitive internal data to its own infrastructure, and in some cases victims paid substantial ransoms.
Authorities are currently aware of roughly 500 successful attacks. Prior to its takedown, the KillSec leak website listed roughly 450 victims.
Investigators are analyzing seized devices and data and tracing KillSec’s criminal proceeds, including cryptocurrency. They hope the evidence will lead to additional victims, attacks, and suspects.
Authorities from Belgium, Finland, Germany, Greece, the Netherlands, Romania, Spain, Switzerland, the UK, and the US took part in the operation, which received support from cybersecurity firms Bitdefender and Group-IB.
Related: Treasury Blacklists Most-Wanted ATM Malware Developer and His Network
Related: Prison Sentence for Former US Soldier Who Hacked AT&T and Verizon
Related: ShinyHunters Defiant After FBI Calls on Members to Come Forward