The number of Cisco devices hacked through the exploitation of an unpatched IOS XE vulnerability has reached approximately 40,000, according to multiple cybersecurity firms.
The exploited vulnerability is CVE-2023-20198, a critical flaw affecting the IOS XE web interface that can be exploited by remote, unauthenticated attackers for privilege escalation.
Cisco has yet to release patches and the company warned that the vulnerability has been exploited as a zero-day since at least mid-September.
CVE-2023-20198 allows threat actors to create high-privileged accounts on targeted devices and take complete control of the system. In some cases, attackers have been observed delivering an implant that enables them to execute arbitrary commands.
Cisco said in some cases the implants were delivered via an older flaw tracked as CVE-2021-1435, but a previously unknown vulnerability may have also been exploited because the implant was also spotted on systems patched against CVE-2021-1435.
Vulnerability intelligence company VulnCheck conducted an internet scan shortly after the zero-day’s existence came to light and found 10,000 compromised switches and routers, but noted that the number would likely increase as its scanning had been ongoing.
While VulnCheck has yet to provide an update, a scan conducted by the internet search engine Censys on October 17 showed 67,000 internet-exposed IOS XE web interfaces, including more than 34,000 hosts that appeared to have been backdoored. Another scan conducted by Censys the next day showed that the number of hacked systems increased to nearly 42,000.
A majority of the compromised Cisco devices appear to be in the United States, followed by the Philippines and Latin America. India, Thailand, Singapore and Australia also have a significant number of infections.

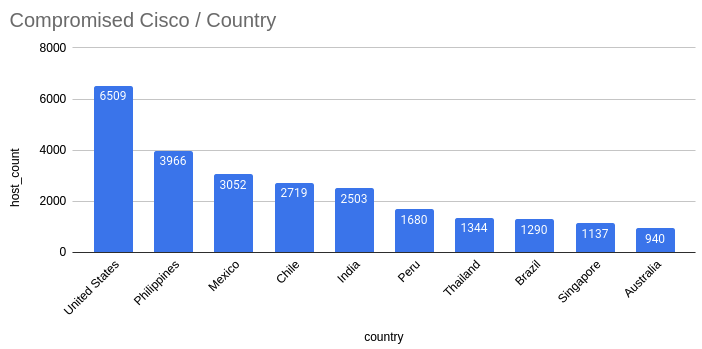
LeakIX, which scans the internet for vulnerable systems, initially reported seeing the malicious implant on roughly 30,000 Cisco devices, but its latest scan detected an additional 10,000 compromised systems.
Threat intelligence company GreyNoise has been using its honeypots to track attack attempts and as of October 19 it has seen attacks originating from 230 unique IP addresses.
Related: Cisco Warns of IOS Software Zero-Day Exploitation Attempts
Related: Cisco ASA Zero-Day Exploited in Akira Ransomware Attacks