Researchers at penetration testing and threat intelligence firm PCA Cyber Security (formerly PCAutomotive) have discovered that critical vulnerabilities affecting a widely used Bluetooth stack could be exploited to remotely hack millions of cars.
The researchers conducted an analysis of the BlueSDK Bluetooth framework developed by OpenSynergy and found several vulnerabilities, including ones that enable remote code execution, bypassing security mechanisms, and information leaks.
They demonstrated how some of these flaws could be chained in what they named a PerfektBlue attack to remotely hack into a car’s infotainment system. From there the attacker can track the vehicle’s location, record audio from inside the car, and obtain the victim’s phonebook data.
The attacker may also be able to move laterally to other systems and potentially take control of functions such as the steering, horn and wipers. While this has not been demonstrated, previous research showed that it is possible for a hacker to move from a car’s infotainment to more critical systems.
The PerfektBlue hack has been demonstrated against recent infotainment models shipped with Mercedes-Benz, Skoda, and Volkswagen cars, as well as products made by another, unnamed OEM that was only recently made aware of the findings.
BlueSDK is present in millions of devices. The list includes not only vehicles, but also mobile phones and other portable gadgets made by dozens of major tech companies.
In order to conduct an attack, the hacker needs to be in range and able to pair their laptop with the targeted infotainment system over Bluetooth. In some cases pairing is possible without any user interaction, while in others pairing requires user confirmation, or it may not be possible at all.

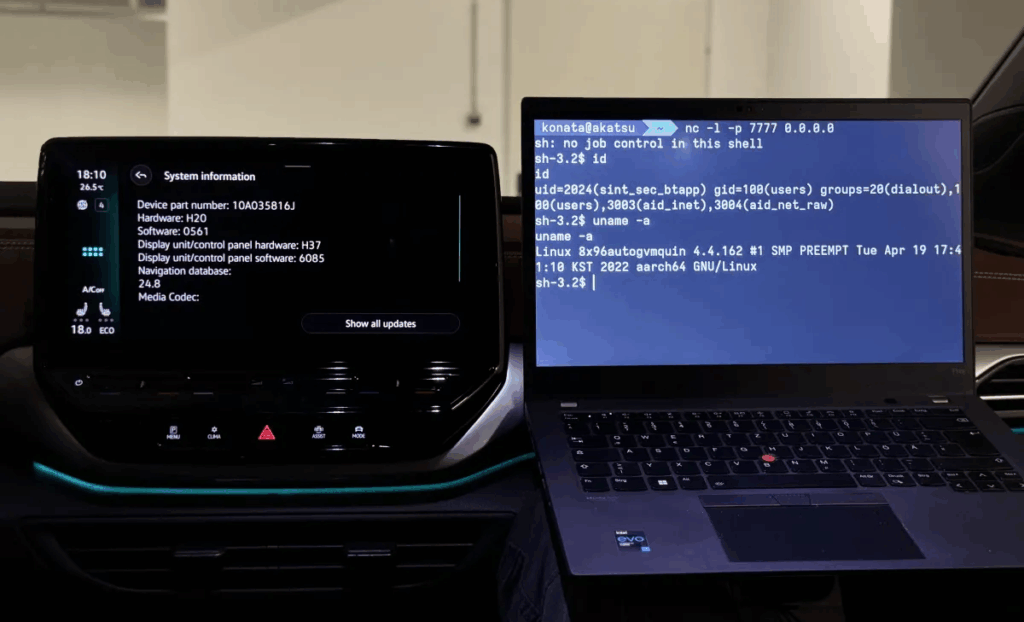
“Essentially, PerfektBlue requires at most 1-click from a user to be exploited over-the-air by an attacker,” PCA Cyber Security explained.
The PerfektBlue vulnerabilities were reported to OpenSynergy back in May 2024 and were assigned the CVE identifiers CVE-2024-45434, CVE-2024-45431, CVE-2024-45432 and CVE-2024-45433.
Patches were created and distributed to customers starting in September 2024, but PCA Cyber Security waited until now to disclose them to ensure that the fixes would be widely deployed.
Earlier this year, PCA Cyber Security disclosed a series of vulnerabilities that could be exploited to remotely hack a Nissan Leaf electric vehicle, including for spying and the physical takeover of several functions.
Related: Hackers Earn $886,000 at Pwn2Own Automotive 2025 for Charger, OS, Infotainment Exploits
Related: Subaru Starlink Vulnerability Exposed Cars to Remote Hacking
Related: 100 Car Dealerships Hit by Supply Chain Attack
Related: Details Disclosed for Mercedes-Benz Infotainment Vulnerabilities