The notorious LockBit cybercrime group has taken credit for the recent ransomware attack that forced the City of Wichita, Kansas, to shut down many of its systems.
The city disclosed the incident on May 6, one day after the intrusion was discovered. Wichita said the hackers had deployed file-encrypting malware on some of its systems.
The incident appears to have impacted water utility, municipal court, cultural, and public transportation payments. The city also announced that public Wi-Fi was not working at the airport, and arrival and departure screens stopped working due to the hack. It’s unclear when these systems would become operational again.
Wichita is apparently still investigating whether any information was stolen during the cyberattack.
The city was added to the LockBit website on May 7, with the cybercriminals threatening to leak files stolen from its systems in seven days, unless a ransom is paid.
The news comes shortly after authorities announced the unmasking of LockBitSupp, the mastermind behind the LockBit ransomware operation.
Dimitry Yuryevich Khoroshev, 31, of Voronezh, Russia, has been charged by the US, where he faces up to 185 years in prison. He has also been sanctioned by the US, UK and Australia. The US is offering up to $10 million for information leading to his arrest.
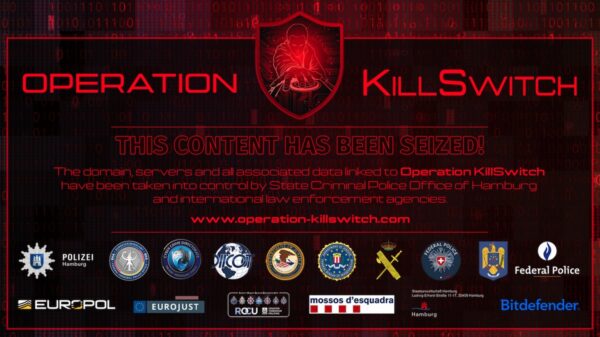
The LockBit operation was severely disrupted in February by an international law enforcement operation.
Just before authorities named Khoroshev as LockBitSupp, threat intelligence firm Cyberint reported that over 50 companies had been added to the new leak site set up by LockBit operators following the takedown.
While this could be a sign of the cybercrime group’s revival following the law enforcement operation, Cyberint said it could also represent a final attempt to “garner attention and revenue before law enforcement permanently dismantles their operations”.
Major ransomware groups announcing a significant campaign before permanently shutting down an operation and re-launching under a new name is not unheard of.
Related: City of Dallas Details Ransomware Attack Impact, Costs
Related: Ransomware Attack Pushes City of Oakland Into State of Emergency
Related: $1.1M Paid to Resolve Ransomware Attack on California County