The integrity of the US voting system is a continuing concern, involving machine tampering, ballot counting, and voter influence. These all have some cybersecurity relevance. Other concerns include accurate voter registration, differing voter ID requirements across states, and the potential for voter fraud where identity verification measures are considered insufficient. Those are a different kettle of issues that are largely although not necessarily outside the scope of cybersecurity and not discussed here.
The Process
Voting: casting and counting
The US voting process is a state-run multi-stage operation. Processes vary by state and county. Most voters mark paper ballots by hand, but here we focus on jurisdictions that use ballot-marking devices for in-person voting, which carry the most cybersecurity relevance.
Furthermore, although voters may have the option for mail-in voting, we’ll focus on Election Day in-person voting via voting machines. Here, the voter indicates the candidate of choice on the voting machine. This machine is pre-certified by the Election Assistance Commission (EAC), and air-gapped for additional security.
The machine prints a paper ballot with the elector’s choice of candidate. This includes a human-readable element that allows the voter to visually check the accuracy of the vote. It usually includes a barcode or QR code containing the same information. The paper ballot is then scanned into the vote-counting part of the voting process. The paper ballot itself remains intact as an ongoing form of verification.
The scanned votes are counted by machine and delivered to the election officials. Further statistical manual checks may be used: does, for example, a small manual count of a portion of the paper ballots statistically conform with the overall machine-counted result?
This sounds straightforward and secure.
Influencing the vote
Received wisdom is that foreign nations attempt to disrupt US elections with influence campaigns targeting the voters. It is believed the primary motivation is to undermine confidence in democratic institutions. This is a valid concern, because lower public trust can lead voters on either side to question the legitimacy of an outcome.
Influence campaigns are particularly relevant to the US. The country is extremely partisan and almost exactly split between just two parties. Throughout this discussion it is worth remembering that small changes to the vote can lead to big changes in the result.
Hard proof of foreign influence campaigns is difficult. Nevertheless, the possibility for and potential effect of influence campaigns remains a serious concern.
Securing the integrity of elections
Voting and counting
US election voting machines are certified by the EAC. This certification is designed to ensure their security and applies to both the voting and counting machines.
Shai Bargil, co-founder and CEO at Sequent, is doubtful. There is no direct correlation of the certification process to the four-year election cycle and certification can occur in any of the four years. The certification process may take a year, but probably less than two years. In the worst case scenario, a voting machine whose certification began in the first year of the electoral cycle will have been sitting, untouched, for two years.
“That’s pretty ridiculous,” comments Bargil. “Software needs to be updated and patched pretty much continuously. In the commercial world we patch our systems every month, but for elections we are trusting software that hasn’t been patched for two years or more. In the final analysis, this EAC certification is pretty much meaningless.”

Additional security is theoretically applied by keeping the machines air-gapped. Air gaps can be bridged by someone who can get close to the target. So, now consider this scenario, which is implausible but possible. Certified machines are often taken to the Voting Village, a hands-on election‑security lab run at DEF CON. It gives security researchers, election officials, and the public legal access to real voting equipment so they can test the security (or insecurity) of them. Some of these machines are still in use in the current election cycle when they are delivered to the Voting Village.
“Basically,” continues Bargil, “every voting machine that has been delivered to a Voting Village has been successfully hacked once the hackers have hands-on access.” Going back to the length of the certification process and the fixed four-year election cycle, it is distinctly possible that the machine used to produce the ballot papers in an election is the same unpatched machine that has already been hacked.
It is equally possible to imagine that the same successful hacker could turn up to vote with everything necessary to repeat his successful hack installed on a USB stick. If this is done early in the morning, every subsequent voter at that machine may be using a compromised system doing who knows what. Implausible? Yes. Possible? Well…
Modern cybersecurity professionals would hesitate to claim voting machines are secure. But the problems don’t end there. The ballots (the slip of paper generated by the voting machine, designed to allow voters to visually verify the accuracy of their votes) are scanned into other machines and totaled before the result emerges at the other end. It’s effectively a black box process certified, possibly a year or more ago, by a third party that hasn’t patched the software for the same period of time.
Worse, while the ballot may provide human-readable confirmation of the voter’s selected candidate, the data scanned by the counting process is usually delivered by a barcode or QR code on the ballot paper. The voter cannot visually verify what is counted by examining a ballot paper produced by a voting machine that may have been hacked.
Bargil says this results in two primary problems. “One is that the voting machines are not to be trusted. The second is that the counting process takes too long and is also not to be trusted.”
The mistake, suggests Christiaan Beek, VP of cyber intelligence at Rapid7, is treating voting machines as the ultimate source of truth. “Treat them as one component in a broader, potentially hostile system,” he says. “Assume that the software may contain vulnerabilities, the firmware may be insecure, the supply chain may be targeted, an administrator account may be compromised, and a determined adversary may eventually gain access.”
His recommendation is to make any compromise as difficult as possible, to limit any blast radius and expose any manipulation, and to provide a way to reconstruct and verify the outcome.
Bargil has his own recommendations to improve security without radically changing the process. The first is to make all software used by the machines open source. “It can still be certified by the EAC, but if it’s open source, it basically means all the academics and security experts that typically review elections can see any potential problems.”
It’s not a 100% guarantee of the security and integrity of the software in use, but, he adds, “If you have open source software, I can use tools to check the code and do my own pentesting. I can use AI to speed the process, and confirm that the EAC and the vendor have done their job properly.”
His second recommendation would ensure the validity of the vote count. The voting machine software should be amended to generate an encrypted voting record sent directly to the counting system and used to count the individual votes.
“It provides evidence that every vote was correctly cast, recorded by the system and counted according to the voter intent: and this is mathematical proof that can be independently verified,” says Bargil, whose company develops verifiable voting software. This would be in addition to the paper ballot rather than simply instead of it.
Interestingly, the Microsoft ElectionGuard project, designed to help governments run secure, auditable and trustworthy elections, also proposes homomorphic encryption of the votes. This could ensure that all votes are counted, not altered, and that no votes were removed nor added to the process. ElectionGuard does not, however, suggest open sourcing the software, even though ElectionGuard itself is open-sourced by Microsoft.
In short, current US voting cannot be considered secure in strict cybersecurity terms, but there are options that would make it more trustworthy. This, however, still leaves the problem of third-party election influence campaigns unresolved. “The harder problems are on the perimeter – voter registration databases, county websites, the email accounts of campaign staff and election workers. Based on what we’ve seen, starting in 2016, this is where the adversaries focus. While the machines get the headlines, the operational layer around them is what actually protects the vote,” says Dave Gerry, CEO at Bugcrowd.
Election influence campaigns
Adam Marrè, former FBI special agent and now CISO at Arctic Wolf, explains the concern. “Elections have long been attractive targets for geopolitical actors because they provide an opportunity to influence public trust, shape political narratives, create division, and undermine confidence in democratic institutions.”
He suggests, “Most election-related activity today is not focused on changing votes. Instead, adversaries often seek to influence perceptions around the election itself,” citing “disinformation campaigns, social media manipulation, cyber espionage, phishing attacks targeting election officials, or attempts to disrupt election-related services.”

Bobby Ford, chief strategy and experience officer at Doppel, agrees with this view. “Today, attackers don’t need to infiltrate election infrastructure to have an impact. They can influence public perception through impersonation, fake websites, and AI-generated misinformation designed to create confusion, evoke urgency, or erode confidence in the process.”
Multiple sources claimed that Russia ran a pro-Trump multi-faceted influence campaign prior to the 2016 election. In 2017, the US intelligence community (CIA, NSA and FBI) said so. In 2019, special counsel Robert Mueller said so. And in 2020, the Senate Intelligence Committee said so.
More recently, in 2024, US intelligence agencies attributed a hack-and-leak operation targeting the Trump campaign to Iran.
Now AI is opening a new potential. “The simplest way to influence an election is to get voters to stay home. The simplest way to do that is with targeted robocalls and robotexts,” comments Alex Quilici, CEO at YouMail. On a relatively small scale, this has already happened with the 2024 Biden impersonation robocall in New Hampshire.
This was a deepfake Biden voice-impersonating automated robocall urging Democrats to stay at home and preserve their vote until the November election. It falsely suggested that their vote would only matter in November, not in the primary. This attack failed (the perpetrator said it was not a serious attack, but an attempt to open people’s eyes to the possibilities of AI), but is widely considered to be a landmark event suggesting an increased use of AI in future influence campaigns, where targeted suppression of one candidate could potentially elevate a different candidate into a winning position.
AI has become the joker in the pack of tools available to any third party wishing to influence the outcome of an election. Always bear in mind the finely balanced US electorate between the two major parties. Any attempt to change the outcome of an election would only require successful influence targeted at a few well-chosen voters.
Throughout this article we have discussed implausible but technically possible attacks on the voting process. We won’t stop now. Consider this hypothesis. On August 12, 2026, Google Search briefly reported that Sam Altman was dead. This was because it had found a ‘vandalized’ Wikipedia entry, and this much of our hypothesis is true.

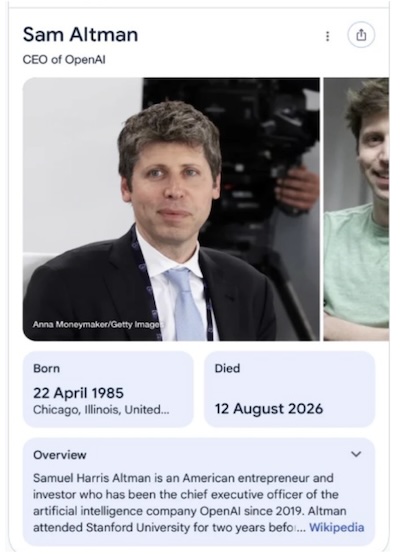
Now imagine how a nation-state could use such an approach against a few selected candidates across the US. ‘Dead’ might be a bit extreme and too easily checked since it is a pure binary fact. Behavior, however, is associated with analog belief – so a campaign promoting a false rumor of insalubrious behavior prior to the vote could affect wide and negative attitudes toward a single candidate. With nation-state resources, this could include large-scale and amplified X tweets, and Facebook and LinkedIn posts. Carefully timed, it could succeed and effectively promote a different preferred candidate before being discovered – and changing a vote is difficult.
Even if an appeal is successful and a complete redo is initiated with the false rumor successfully countered (is that even possible since rumors tend to linger in the mind?), Marrè’s initial suggestion that the purpose of influence campaigns is to ‘undermine confidence in democratic institutions’ is successful.
As Ford suggests, “As AI makes these attacks more scalable and personalized, election security has become just as much about protecting trust as it is about protecting technology. That means defending election officials, campaigns, and trusted information sources alongside the infrastructure itself.”
Casey Erikson, director of penetration testing at NRLabs, adds, “In the end, every architectural decision carries a tradeoff. The objective is not to eliminate risk but to constrain it. It becomes about access control. Verifiable backups are essential, redundancy at multiple layers is best.”
Summary
The purpose of this discussion is not to criticize the US voting system, but to examine it through a cybersecurity lens. Looking at implausible but technically possible attacks shows that, in strict cybersecurity terms, no part of the process can be considered beyond compromise.
That does not mean US elections have been compromised. Election officials rely on layered safeguards, including pre-election testing, chain-of-custody controls, bipartisan poll workers, and post-election audits of paper ballots, and there is no evidence that machine tampering has changed the outcome of a US election.
A similar examination of voting systems elsewhere would likely reach the same conclusion. In the current digital and geopolitical climate, an absolutely secure election is essentially impossible – which is why verifiability, auditing, and public trust matter as much as the technology itself.
Related: Denmark Blames Russia for Cyberattacks Ahead of Elections and on Water Utility
Related: US Cyber Agency Puts Election Security Staffers Who Worked With the States on Leave
Related: US Cyber Agency’s Future Role in Elections Remains Murky Under the Trump Administration
Related: The Fourth Battlefield: The Growing Role of Cyber Operations in Global Conflict