Swedish state-owned power grid operator Svenska kraftnät on Monday confirmed that it fell victim to a cyberattack that resulted in a data breach.
The incident, the company said, was discovered on Saturday and affected an isolated, external file transfer solution, but not the power grid.
The country’s electricity supply has not been affected by the attack, the public utility’s Chief Information Security Officer Cem Göcören said.
Since learning of the attack, Svenska kraftnät has been scrambling to understand its scope and impact. The incident has been reported to the authorities, the company said.
Göcören pointed out that no additional information on the incident and the threat actor responsible would be shared now, given the ongoing investigation. However, no critical systems were impacted, the CISO said.
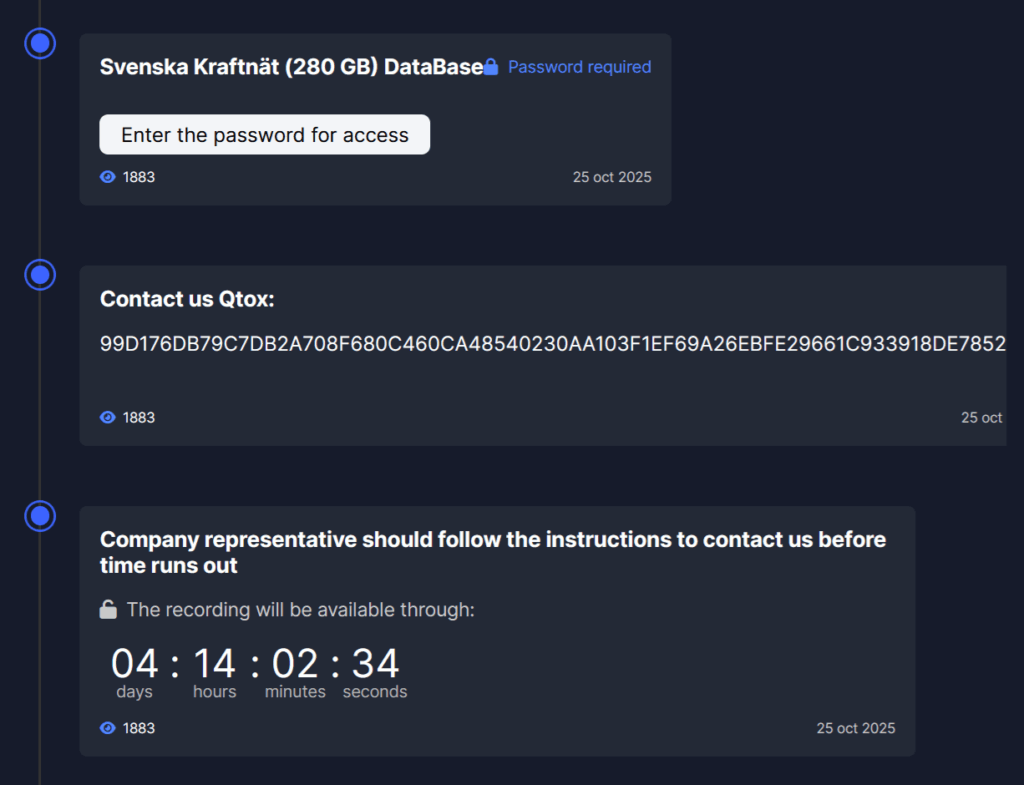
The data breach was disclosed shortly after the Everest ransomware group added Svenska kraftnät to its Tor-based leak site, which essentially confirms that the threat actor was responsible for the incident.
Everest says it stole roughly 280 gigabytes of data from the power grid operator, threatening to leak it online unless the public utility complies with its demands.

It is unclear for now what type of data Everest exfiltrated from Svenska kraftnät, but the company said it would provide additional details on the matter as its investigation progresses.
Created in 1992 and headquartered in Sundbyberg, near Sweden’s capital Stockholm, Svenska kraftnät owns and manages 17,500 km of power lines and owns 28% of the pan-European power exchange Nord Pool.
The Everest ransomware group has been active since December 2020, engaging in double extortion tactics, but lately focused on data exfiltration and extortion. Recently, it claimed the Collins Aerospace hack that disrupted major European airports.
Related: Ransomware Payments Dropped in Q3 2025: Analysis
Related: Russian Government Now Actively Managing Cybercrime Groups: Security Firm
Related: Fencing and Pet Company Jewett-Cameron Hit by Ransomware