Grafana confirmed suffering a data breach on Sunday, two days after a cybercrime group listed the company on its leak website.
The open source visualization and analytics software provider said the intrusion was possible due to a compromised token that granted access to the Grafana Labs GitHub environment.
Grafana admitted that the hackers managed to download its codebase, but said no personal or customer information was stolen and the incident has not impacted customer systems or operations.
The company said the attackers demanded a ransom to prevent the source code from being leaked, but it has decided not to pay up.
The compromised credentials have been reset, and a forensic analysis is being conducted. Grafana has promised to share additional details when the investigation is completed.

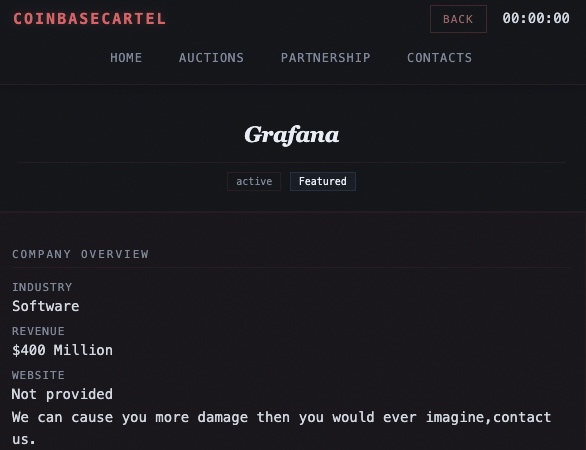
Grafana was listed on the website of the cybercrime group Coinbase Cartel on May 15, but no data appears to have been leaked at the time of writing.
“We can cause you more damage than you would ever imagine,” the hackers said.
The gang, active since September 2025, does not use file-encrypting ransomware. Instead, it demands a ransom payment after stealing sensitive data from victims. The Coinbase Cartel website currently lists 105 victims.
Cybersecurity companies say Coinbase Cartel is linked to ShinyHunters, Scattered Spider, and Lapsus$, whose members have been collaborating since at least mid-2025, with some evidence pointing to a possible partnership dating back to 2024.
The alliance has been conducting a major data theft campaign, using the ShinyHunters name to sign and claim intrusions against several high-profile companies, including Instructure, Vimeo, Wynn Resorts, Vercel, and Medtronic.
Related: TeamPCP Ups the Game, Releases Shai-Hulud Worm’s Source Code
Related: Trellix Source Code Repository Breached
Related: GrafanaGhost: Attackers Can Abuse Grafana to Leak Enterprise Data