Google has released a security update for its Chrome browser, addressing a zero-day vulnerability that the company confirms is actively being exploited in the wild.
Several exploited zero-day vulnerabilities have been patched by the internet giant in Chrome this year. However, the company has always shared a brief description of the flaw when announcing patches.
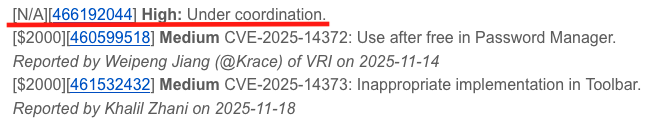
At the time of writing, the latest Chrome zero-day does not have a CVE identifier, and it’s unclear which component of the browser it affects. The company is currently identifying it using a bug tracker ID (466192044) and has marked it as ‘under coordination’.
It’s also unclear who discovered the vulnerability and when it was reported to Google. The only piece of information that is available is that the security hole has a ‘high severity’ rating.

Based on historical trends of actively exploited Chrome zero-days, this flaw may be a memory corruption issue (potentially type confusion or use-after-free) within the V8 JavaScript engine or a related component.
These types of vulnerabilities can typically be leveraged for a sandbox escape or remote code execution.
Chrome zero-days are frequently exploited by government-sponsored espionage campaigns that utilize sophisticated commercial spyware. This suggests that the mysterious vulnerability may have been part of a targeted, rather than widespread, attack campaign.
The zero-day has been patched with a Chrome 143 update that also addresses two medium-severity issues: a use-after-free in the browser’s password manager, and an inappropriate implementation flaw in the toolbar component.
Each of these security holes earned the reporting researchers a $2,000 bug bounty.
UPDATE: The mysterious Chrome vulnerability is CVE-2025-14174 and it has been tied to two newly patched Apple zero-days.
Related: Google Fortifies Chrome Agentic AI Against Indirect Prompt Injection Attacks
Related: Chrome, Edge Extensions Caught Tracking Users, Creating Backdoors
Related: Chrome to Turn HTTPS on by Default for Public Sites

















