Cyber agencies from several countries have published joint guidance outlining principles for the safe and secure use of artificial intelligence in operational technology (OT) environments, particularly in critical infrastructure.
The guidance, published on the website of the cybersecurity agency CISA, was authored by government organizations in the United States, the United Kingdom, Canada, Germany, the Netherlands, and New Zealand.
Integrating AI with industrial control systems (ICS) and other OT can have significant benefits. The agencies have provided several examples of use cases.
For instance, in the case of field devices such as sensors and actuators, the data they generate can be used to train AI models and identify significant deviations. In the case of programmable logic controllers (PLCs) and remote terminal units (RTUs), AI can be leveraged for classifying load balancing and anomaly detection.
[Read: Over 370 Organizations Take Part in GridEx VIII Grid Security Exercise ]
Supervisory control and data acquisition (SCADA), distributed control system (DCS), and human-machine interface (HMI) systems can benefit from AI models analyzing data to detect early signs of equipment anomalies.
AI can also be used for predicting equipment maintenance requirements, providing recommendations for operator decision-making, optimizing workflows, and threat detection based on IT/OT data analysis.
The 25-page document, titled ‘Principles for the Secure Integration of Artificial Intelligence in Operational Technology’, describes four key principles for securely integrating AI into OT systems.
The first principle focuses on understanding AI, including its unique risks and potential impact on OT. For instance, the use of artificial intelligence can introduce cybersecurity risks that lead to system compromise, disruptions, financial loss, and functional safety impact.
In addition, low-quality training data, model drifts, and other issues can lead to inaccurate alerts, reduced system availability, safety risks, and reputational damage.
Many of the issues associated with the use of AI can be addressed by clearly defining the roles and responsibilities of AI makers, OT suppliers, and managed service providers throughout the system’s lifecycle.
In addition, the education of personnel on AI is also critical, as employees’ overreliance on AI automation can lead to skill erosion and skill gaps — workers no longer being able to manage systems during AI failures, or incorrectly managing a situation due to the misinterpretation of AI outputs.

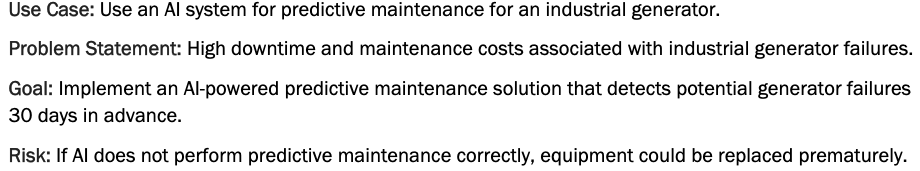
The second principle outlined by the government agencies focuses on determining the business use case of AI. A business needs to assess whether AI is the right solution for their needs compared to other available solutions.
Critical infrastructure operators must then address data security challenges, and understand the role of OT vendors in AI integration.
The third principle focuses on AI governance and assurance, including establishing governance mechanisms for AI, integrating AI into existing security frameworks, and conducting testing and evaluations. Organizations also need to focus on regulatory and compliance considerations.
The last principle covers oversight and failsafe practices: ensuring monitoring and oversight mechanisms, and embedding safety and failsafe systems.
“By adhering to these principles and continuously monitoring, validating, and refining AI models, critical infrastructure owners and operators can achieve a balanced integration of AI into the OT environments that control vital public services,” the authoring agencies said.
Related: CISA Warns of ScadaBR Vulnerability After Hacktivist ICS Attack
Related: Japan Issues OT Security Guidance for Semiconductor Factories