Fieldtex Products, a US company that provides contract sewing and medical supply fulfillment services, has disclosed a data breach after it was targeted by a notorious ransomware group.
In a data security incident notice posted on its website on November 20, Fieldtex said it detected unauthorized access to its systems in mid-August. An investigation showed that hackers may have gained access to “a limited amount of protected health information”.
Fieldtex specializes in commercial sewing services and manufacturing soft-sided carrying cases for the medical and military sectors. It also distributes first aid and medical supplies through a dedicated division.
[ Read: SecurityWeek coverage of healthcare data breaches ]
The compromised information, provided to the company by members of health plans that received its healthcare-related products, includes names, addresses, dates of birth, insurance member ID numbers, plan names, effective terms, and gender.
The healthcare data breach tracker maintained by the US Department of Health and Human Services revealed this week that the Fieldtex data breach has impacted 238,615 individuals.

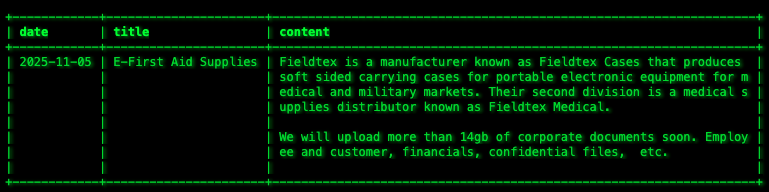
The Akira ransomware group took credit for the Fieldtex hack on November 5.
The cybercriminals listed Fieldtex’s E-First Aid Supplies division on their Tor-based leak website, claiming to have stolen more than 14 Gb of corporate documents, including files containing employee, customer, and financial information.
Akira said it would make the stolen data available “soon”, but at the time of writing it does not appear to have published any files on its leak site.
Related: Over 300,000 Individuals Impacted by Vitas Hospice Data Breach
Related: Tri-Century Eye Care Data Breach Impacts 200,000 Individuals
Related: Synnovis Confirms Patient Information Stolen in Disruptive Ransomware Attack













