Title insurance giant Fidelity National Financial (FNF) is experiencing service disruptions after it has taken down multiple systems to contain a cyberattack.
The incident, FNF said in a Form 8-K filing with the Securities and Exchange Commission (SEC) just before Thanksgiving, has impacted “title insurance, escrow and other title-related services, mortgage transaction services, and technology to the real estate and mortgage industries”.
According to the company, its F&G Annuities & Life subsidiary, which provides insurance solutions, was not affected.
FNF says that an investigation was immediately launched into the incident and that law enforcement was also notified.
To date, the investigation has determined that the attackers gained unauthorized access to certain systems and that some credentials were stolen.
While FNF did not specify what type of cyberattack it fell victim to, the fact that it has shut down systems to contain the incident suggests that ransomware might have been involved.
In fact, the notorious Alphv/BlackCat ransomware group has already taken responsibility for the attack, adding FNF to their leak site.

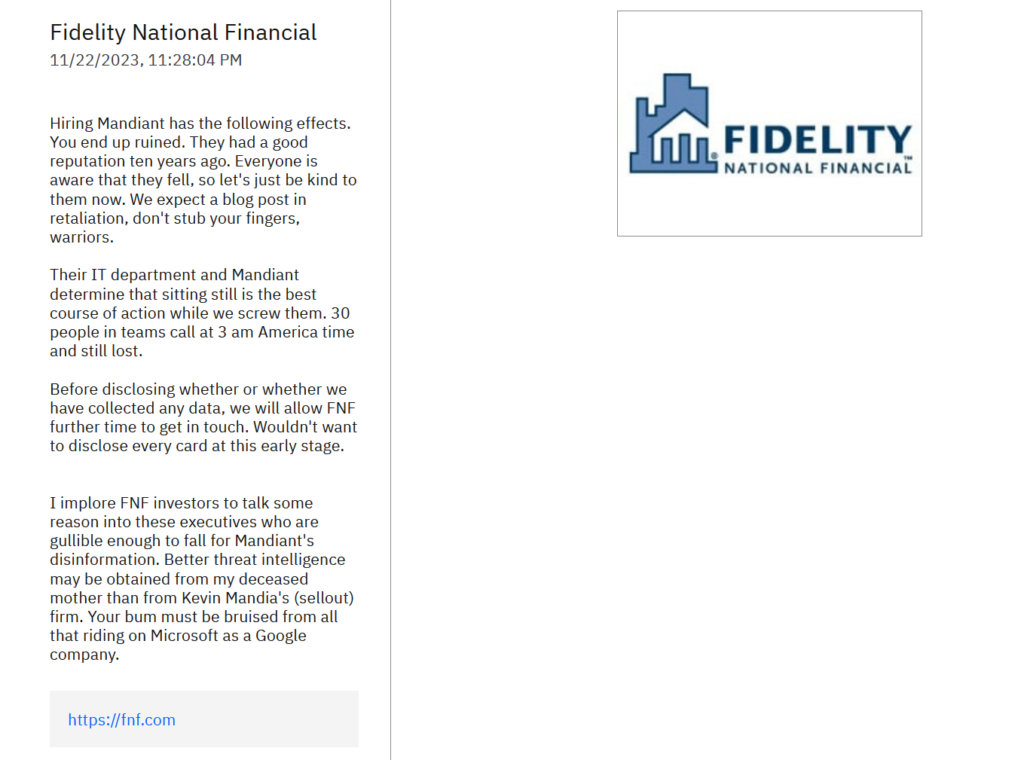
The threat actor did not specify whether any information was exfiltrated from the victim’s network, claiming it would reveal this later, if FNF does not pay a ransom.
FNF is one of the largest title insurance entities and underwriters groups in the US. It also offers settlement services to the real estate and mortgage industries.
Related: Canadian Military, Police Impacted by Data Breach at Moving Companies
Related: Yamaha Motor Confirms Data Breach Following Ransomware Attack
Related: Western Digital Confirms Ransomware Group Stole Customer Information














