The European Commission, the EU’s executive branch, has confirmed being targeted in a cyberattack that impacted its cloud infrastructure, as hackers claimed to have stolen hundreds of gigabytes of data.
In a statement issued on Friday, the European Commission (EC) said the attack affected cloud infrastructure hosting its web presence on the Europa.eu platform, but noted that its public websites were not disrupted.
“Early findings of our ongoing investigation suggest that data have been taken from those websites. The Commission is duly notifying the Union entities who might have been affected by the incident. The Commission’s services are still investigating the full impact of the incident,” the Commission stated.
It added, “The Commission’s internal systems were not affected by the cyber-attack.”

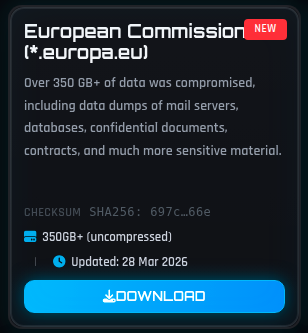
A message posted over the weekend on the website of the ShinyHunters cyber extortion group claimed more than 350GB of data were stolen, “including data dumps of mail servers, databases, confidential documents, contracts, and much more sensitive material”.
Bleeping Computer learned from the hackers that they targeted the EC’s AWS accounts.
AWS stated that it “did not experience a security event”, noting that its services “operated as designed”.
This statement indicates that the attackers leveraged a compromised account or a security misconfiguration to gain access to the Commission’s systems, rather than by exploiting a vulnerability in AWS products or services.
This is the second data breach confirmed by the EC this year. In February, CERT-EU reported discovering evidence of an intrusion into the Commission’s IT infrastructure, with hackers potentially accessing personal information belonging to some staff members.
Related: Poland Faced a Surge in Cyberattacks in 2025, Including a Major Assault on the Energy Sector
Related: EU Sanctions Chinese, Iranian Firms Supporting Hacking Operations
Related: EU Plans Phase Out of High Risk Telecom Suppliers, in Proposals Seen as Targeting China