German industrial automation solutions provider Wago has released patches for several of its programmable logic controllers (PLCs) to address four vulnerabilities, including ones that can be exploited to take full control of the targeted device.
The vulnerabilities were discovered by Ryan Pickren from the Georgia Institute of Technology’s Cyber-Physical Security Lab. The issues were identified by the researcher as part of a PhD project on the security of industrial control systems (ICS).
Pickren previously earned significant rewards from Apple for camera hacking vulnerabilities and an exploit that could have been leveraged to hack a user’s online accounts and webcam.
During the analysis of Wago PLCs, the researcher discovered several vulnerabilities in the web-based management interface designed for administering, commissioning and updating devices.

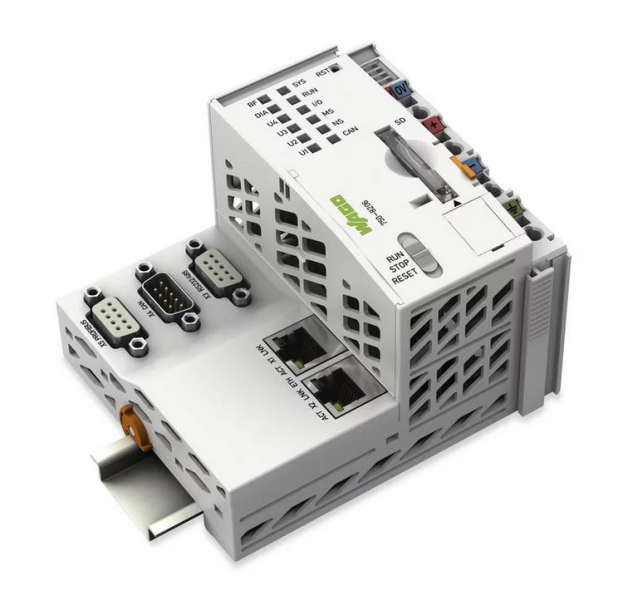
Germany’s CERT@VDE has published an advisory that describes the vulnerabilities and shares information on impacted products and versions.
Two of the flaws have been assigned a critical severity rating based on their CVSS score. One of them, a missing authentication issue tracked as CVE-2022-45138, can be exploited by an unauthenticated attacker to read and set some device parameters, which can lead to a full compromise of the controller.
The second critical vulnerability, CVE-2022-45140, allows an unauthenticated attacker to write arbitrary data with root privileges, which can result in arbitrary code execution and a full system compromise.
In addition, two medium-severity vulnerabilities have been found by Pickren. One of them can be exploited for cross-site scripting (XSS) attacks and the other can lead to information disclosure with limited impact.
“These bugs can be chained together and weaponized in two different ways: 1) direct network access (I.e. the adversary is within the ICS or is attacking an Internet-facing device) or 2) Via cross-origin web requests (I.e. the adversary lures somebody within the ICS into viewing their malicious website). Neither scenario requires any user-interaction (besides just visiting the site) or permissions. The chain is completely unauthenticated,” Pickren told SecurityWeek.
In a real-world attack, a threat actor could exploit these vulnerabilities to maliciously control actuators, falsify sensor measurements, and disable all safety controls, the researcher explained.
Pickren said these vulnerabilities are part of a much larger trend in ICS security that will be described in detail in an upcoming academic paper.
Related: Vulnerabilities in WAGO Devices Expose Industrial Firms to Remote Attacks
Related: WAGO Controller Flaws Can Allow Hackers to Disrupt Industrial Processes
Related: Tens of Vulnerabilities Expose WAGO Controllers, HMI Panels to Attacks