The Glove Stealer malware leverages a recently disclosed App-Bound encryption bypass method in attacks.

Hi, what are you looking for?


The Glove Stealer malware leverages a recently disclosed App-Bound encryption bypass method in attacks.
Threat actors have hijacked over 70,000 domains, including known brands and government entities, because of failed domain ownership verification.
Over 4 million WordPress websites were impacted by a critical Really Simple Security plugin vulnerability providing full administrative access.
The Chinese APT behind the LightSpy iOS backdoor has expanded its toolset with DeepData, a modular Windows-based surveillance framework.
Iran-linked Charming Kitten hackers have been running a ‘dream job’ campaign targeting the aerospace industry with the SnailResin malware.
Cyber risk management solutions provider Bitsight is acquiring threat intelligence firm Cybersixgill for $115 million.
CISA and the FBI have confirmed that Chinese hackers compromised the networks of telecommunications companies to spy on specific targets.
Robert Purbeck was sentenced to 10 years in prison for stealing the personal information of over 132,000 people.
The exploit for a new zero-day vulnerability in Windows is executed by deleting files, drag-and-dropping them, or right clicking on them.
Most of the top frequently exploited vulnerabilities in 2023 were initially exploited as zero-days, according to data from government agencies.
Ivanti has released fixes for dozens of vulnerabilities in Endpoint Manager, Avalanche, Connect Secure, Policy Secure, and Secure Access Client.
Zoom Apps security updates resolve six vulnerabilities and Chrome 131 stable is rolling out with 12 security fixes.
Citrix and Fortinet have released patches for multiple vulnerabilities, including high-severity bugs in NetScaler and FortiOS.
Cybersecurity incident impacts Giant Food, Hannaford, and other Ahold Delhaize USA brands, including pharmacies and e-commerce services.
SAP has released eight new security notes on November 2024 patch day, including one addressing a high-severity vulnerability in Web Dispatcher.
Hot Topic has suffered a data breach impacting approximately 57 million unique email addresses and the personal information of roughly 25 million.
A new feature in the latest iOS release reportedly reboots locked devices that have not been unlocked for longer periods of time.
The FBI is seeing an increase in threat actors using fake emergency data requests to harvest information from US companies.
Forth says the personal information of 1.5 million people was compromised in a May 2024 data breach.
Veeam has released a hotfix for a high-severity authentication bypass vulnerability in Backup Enterprise Manager.

Threat actors have started targeting CVE-2026-21589, a critical vulnerability in Atlassian’s self-hosted Data Center products.
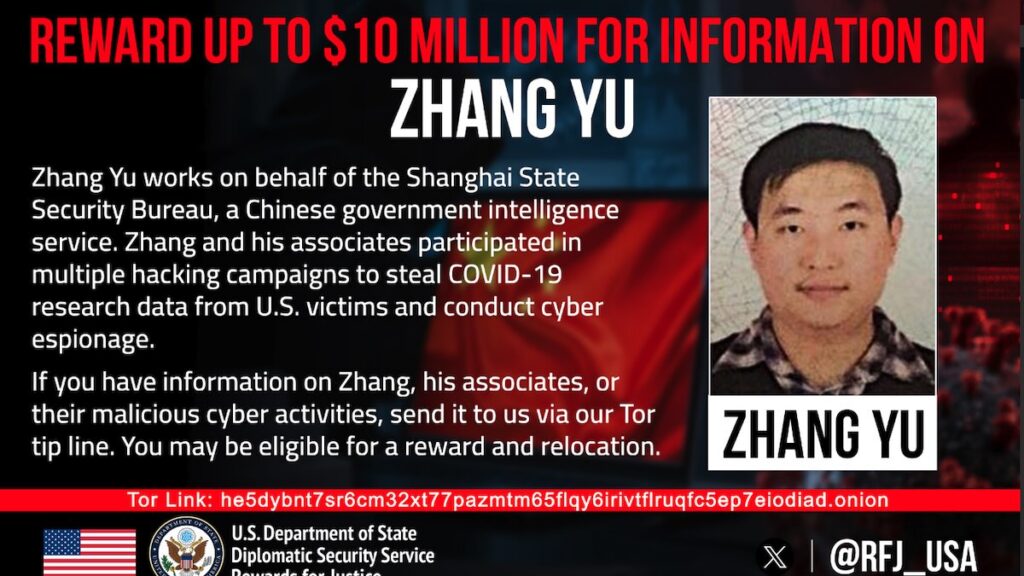
Zhang Yu was charged alongside Xu Zewei, who was extradited from Italy to the US in April 2026.