An updated version of the njRAT remote access Trojan (RAT) is capable of encrypting files and stealing virtual currencies from crypto-wallets, Zscaler warns.

Hi, what are you looking for?


An updated version of the njRAT remote access Trojan (RAT) is capable of encrypting files and stealing virtual currencies from crypto-wallets, Zscaler warns.
While under heavy fire for the user
Apple this week released a new set of security patches to address tens of vulnerabilities impacting macOS, iOS, watchOS, and t
Authorities this week arrested 20 individuals in Italy and Romania for their role in a banking phishing scam that defrauded bank customers of €1...
A recently discovered credential stealing malware is masquerading as Kaspersky Antivirus and spreading via infected USB drives, according to threat detection firm Cybereason.
The banking Trojan known as Panda Banker is now targeting financial institutions in Japan for what appears to be first time.
In macOS High Sierra, the passwords used for Apple File System (APFS)-encrypted external drives are logged and kept in on-disk log files, a security...
Facebook has announced a series of changes to its developer platform to implement tighter user privacy controls and limit how apps can access user...
Malicious crypto-miners have invaded the threat landscape over the past year, fueled by a massive increase in the value of crypto-currency.
A recently discovered malware family written using the Golang (Go) programming language is targeting Linux servers and using a different binary for each attack,...
In recently observed attacks, the jRAT backdoor was using crypter services hosted on the dark web to evade detection, Trustwave security researchers have discovered.
Mozilla today unveiled the "Facebook Container Extension", a new browser extension designed to help Firefox users reduce the ability of Facebook to track their...
A newly discovered Microsoft Office document exploit builder kit has been used for the distribution of a variety of malicious payloads, including banking Trojans...
An attack leveraging the compromised website of a Hong Kong telecommunications company is using a recently patched Flash vulnerability that has been exploited by...
Drupal announced plans to release a security update for Drupal 7.x, 8.3.x, 8.4.x, and 8.5.x on March 28, 2018, aimed at addressing a highly...
A recently observed variant of the TrickBot banking Trojan
The cost of having an organization targeted by a distributed denial of service (DDoS) attack for an hour is as low as $10, cybersecurity...
An Iran-linked cyber-espionage group has been using new malware and data exfiltration techniques in recent attacks, security firm Nyotron has discovered.
A newly discovered Android Trojan is abusing Telegram’s Bot API to communicate with the command and control (C&C) server and to exfiltrate data, Palo...
Attackers can use online sandbox services to exfiltrate data from an isolated network, a SafeBreach security researcher has discovered.
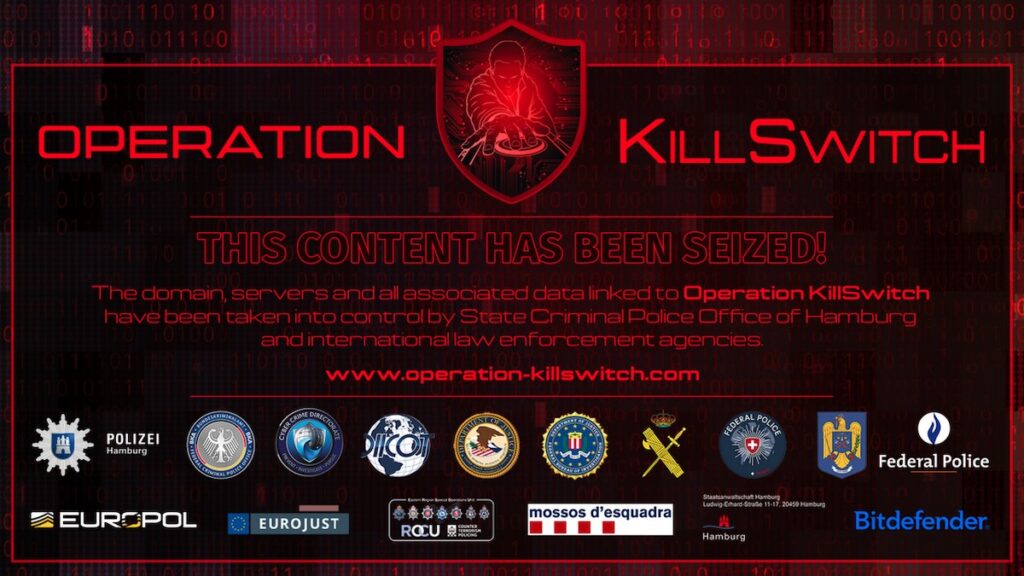
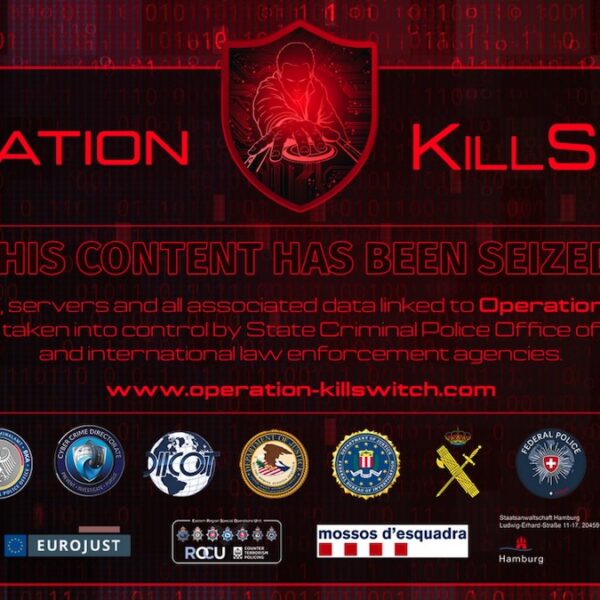
Police took control of KillSec’s leak site and secured at least 110 terabytes of data stolen from victims.
Rob Juncker is chief product and technology officer at Mimecast. Is he a hacker? “Unequivocally yes,” he says.