A Massachusetts man pleaded guilty to his role in an ATM “jackpotting” operation, the United States Department of Justice announced this week.

Hi, what are you looking for?


A Massachusetts man pleaded guilty to his role in an ATM “jackpotting” operation, the United States Department of Justice announced this week.
The author of a newly discovered malware downloader allows interested parties to set up a botshop and build a malware distribution network, Netscout Arbor...
A newly discovered attack against Google Home and Chromecast devices can reveal a user’s precise physical location, a security researcher has discovered.
Sunnyvale, California – based endpoint security firm CrowdStrike today announced that it has secured over $200 million through a Series E round of financing,...
A newly detailed Android remote access Trojan (RAT) is leveraging Telegram’s bot functionality to control infected devices, ESET reveals.
The Betabot Trojan is being spread in a multi-stage attack that starts with malicious Office documents attempting to exploit a 17-year old vulnerability.
A newly added “Endpoint Verification” feature in G Suite provides administrators with increased visibility into the computers that have access to corporate data.
Malware-laden Syscoin releases were up for download on an official GitHub repository after hackers managed to compromise an account and replace legitimate Windows installers.
The number of cyber-attacks targeting Singapore skyrocketed from June 11 to June 12, during the meeting between U.S. President Donald Trump and North Korean...
A newly discovered attack relying on malicious Word documents and PowerShell scripts appears related to the MuddyWater cyber-espionage campaign, Trend Micro reports.
Microsoft this week patched a remote code execution vulnerability affecting the wimgapi library, which is used to perform operations on Windows Imaging Format (WIM)...
GnuPG recently addressed an input sanitization vulnerability where a remote attacker could spoof arbitrary signatures.
One of the vulnerabilities Microsoft addressed with the June 2018 security patches was a flaw in Cortana that could allow an attacker to elevate...
A newly discovered banking Trojan targeting Android 7 and 8 versions is using the same command and control (C&C) server as LokiBot, Threat Fabric...
Exploit kits (EKs) might not be as dominant as they were several years ago, but they continue to exist and most of them already...
Google this week detailed plans to completely remove the inline installation of Chrome extensions from its web browser by the end of the year.
Of the ten Security Notes in SAP’s June 2018 Security Patch Day, five were updates for previously released Notes, including two rated Hot News...
A recently discovered piece of crypto-currency miner malware isn’t only abusing a National Security Agency-linked remote code execution exploit to spread, but also abuses...
The popularity of crypto-currency malware has been skyrocketing over the past year, and the segment appears to have been highly lucrative for cybercriminals, a...
Crestron recently addressed a command injection vulnerability in the console service preinstalled on the Digital Graphics Engine 100 (DGE-100) and other hardware controllers made...
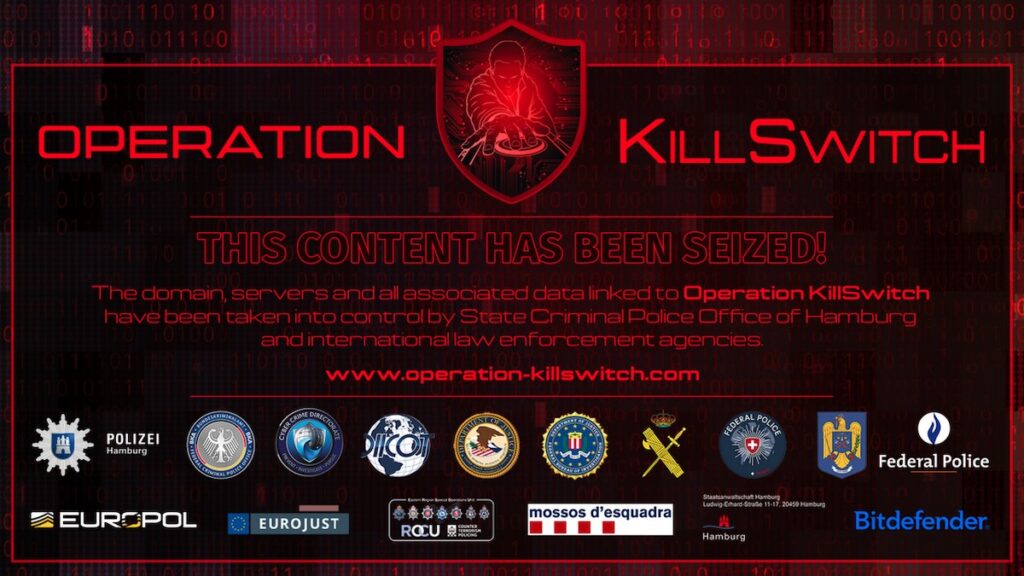
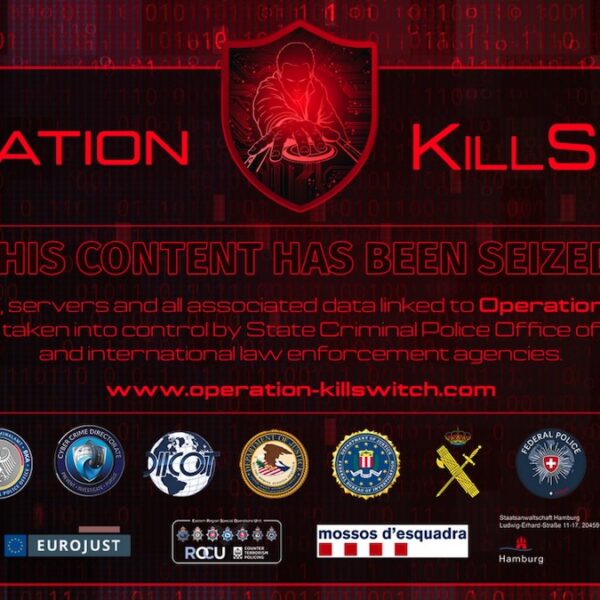
Police took control of KillSec’s leak site and secured at least 110 terabytes of data stolen from victims.
Fifteen years after coining the framework, John Kindervag insists zero trust still works in the AI era—if you get the implementation right.