CISA will remain operational during the DHS shutdown that commenced at 12:01 a.m. on Saturday, February 14, 2026, although at a reduced capacity. KEV is one area that remains.
Although the Antideficiency Act prohibits federal agencies from spending money not appropriated by Congress, it doesn’t mean that staff cannot work – only that they cannot be paid and can only work in areas that are ‘excepted’ by the Act. Staff are basically furloughed.
Ironically, the DHS ICE operations (the primary political cause of the shutdown) is not affected by the shutdown. Its funding comes not from Congress approval, but from the President’s One Big Beautiful Bill Act, while its operations are considered as excepted within the Antideficiency Act.
CISA, however, can be considered as collateral damage. It is affected by the shutdown but intends to maintain as much operational capability as possible. While its staff cannot be paid (and are technically all furloughed), it is requiring 888 of its current workforce of 2,341 staff to remain in situ and at their desks (without pay) in those excepted areas. Those sent home can be recalled if their presence is deemed necessary to protect human life, property, or national security. This could, for example, include ransomware attacks against critical industries, or widespread abuse of a newly discovered vulnerability, as happened with log4j.
Recalls would probably be limited to teams with specific knowledge of the specific excepted threat being handled. Those teams would also be working without pay.
The result is that fewer CISA staff will be operational through the shutdown in fewer areas and will be less personally incentivized. New operational projects are prohibited, and existing projects will be curtailed. The complexity of what can and cannot be undertaken can be seen in two of the agencies’ most visible operations: CIRCIA and the KEV Catalog.
Work to finalize the CIRCIA cyber incident reporting rule will likely be halted because it is regulatory work and not directly related to national security or active cybersecurity threats.
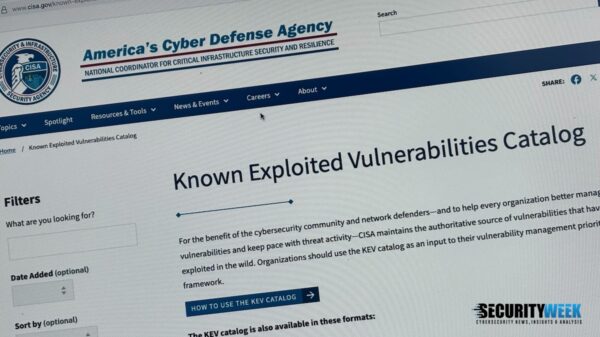
The KEV Catalog, however, lists exploited vulnerabilities that FCEB agencies (effectively, the critical industries) are required to patch. The existing KEV Catalog will remain online through the shutdown. A new and currently exploited vulnerability targeting critical industries and potentially harming life, property or national security would be excepted from the Antideficiency Act – and could be added to the existing KEV Catalog.
The remaining smaller workforce will need to find the time and prioritize what to do. Updating the KEV is time intensive. CISA analysts need to validate the exploitation, understand the availability of a patch, and liaise with federal agencies. Reaction is likely to be slower, even for excepted vulnerability reporting. Recognition and inclusion of older vulnerabilities that have been exploited in the past would likely be given less priority and be delayed.
Enforcing FCEB compliance with KEV would probably not be an excepted operation. Issuing reminders and enforcement notices would be prohibited. So, while the KEV will continue, oversight of critical industries’ compliance with it would be at least weakened if not halted.
Since CISA’s work is primarily to raise and ensure the cybersecurity of FCEB agencies, extending to the critical infrastructure, its work (or during the shutdown, its lack of work) could be considered as not directly affecting general private-sector businesses. This is partly, but only partly, true. CIRCIA, for example, is only relevant to the critical industries within CISA’s remit.
The KEV, however, with its online availability to everyone, has become a primary source of vulnerability remediation information for all cybersecurity practitioners, and will continue to be updated and will remain important to all global businesses. The lights will remain on in CISA during the shutdown, but with fewer operational bulbs.
Meanwhile, as acting CISA leader Madhu Gottumukkala recently commented, “When the government shuts down, our adversaries do not.”
Related: New Paper and Tool Help Security Teams Move Beyond Blind Reliance on CISA’s KEV Catalog
Related: CISA KEV Catalog Expanded 20% in 2025, Topping 1,480 Entries
Related: Exploitation Long Known for Most of CISA’s Latest KEV Additions
Related: Financial Organizations Urge CISA to Revise Proposed CIRCIA Implementation