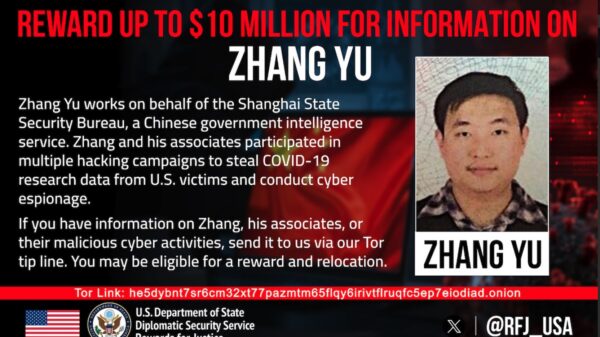
Microsoft threat hunters warned Wednesday of a significant shift in tactics by Silk Typhoon, a Chinese government espionage group linked to recent US Treasury hacks. The group is now targeting companies in the global IT supply chain, including IT services, remote monitoring and management firms and managed service providers.
Instead of going after high-profile cloud services, Microsoft said it caught the threat actor using stolen API keys and compromised credentials to breach a range of companies in the IT supply chain to extend their reach to downstream customer environments.
According to documentation from Redmond’s threat intelligence team, the Chinese government-backed hacking team uses these IT supply chain entry points to conduct extensive reconnaissance, collect sensitive data, and move laterally within victim networks.
The researchers warned that the attackers have a sophisticated understanding of both on-premises and cloud environments, even exploiting tools like Microsoft’s Entra Connect (formerly AADConnect) to further escalate privileges.
While Silk Typhoon has not directly targeted Microsoft cloud services, the company warns that the latest targeting of the IT supply chain signals a wider risk: any organization using common IT solutions without robust patching or secure credential management is vulnerable.
Historically, Silk Typhoon has been linked to a range of successful exploits hitting Microsoft Exchange servers, VPN products and firewall appliances. In the breach of US Treasury Department, the group spied on the foreign investment and sanctions offices and exploited flaws in BeyondTrust and PostgreSQL software.
In its latest operations, Microsoft now warns that the group is abusing API keys from privilege access management and cloud app providers to facilitate lateral movement and data exfiltration, hitting sectors like state and local government, IT services, and financial institutions.
“This threat actor holds one of the largest targeting footprints among Chinese threat actors,” Microsoft declared, warning that Silk Typhoon is well-resourced and capable of quickly pouncing on zero-day discoveries in a wide range of software products.
“Silk Typhoon has shown proficiency in understanding how cloud environments are deployed and configured, allowing them to successfully move laterally, maintain persistence, and exfiltrate data quickly within victim environments,” the researchers explained, nothing that the hacking team has used a myriad of web shells that allow them to execute commands, maintain persistence, and exfiltrate data from victim environments.
Microsoft also observed the use of password spray attacks and other password abuse techniques, including discovering passwords through reconnaissance. “In this reconnaissance activity, Silk Typhoon leveraged leaked corporate passwords on public repositories, such as GitHub, and were successfully authenticated to the corporate account.”
The hackers were also caught abusing service principals and OAuth applications with administrative permissions to perform email, OneDrive, and SharePoint data exfiltration via MSGraph.
“Silk Typhoon has been observed gaining access to an application that was already consented within the tenant to harvest email data and adding their own passwords to the application. Using this access, the actors can steal email information via the MSGraph API,” Microsoft noted.
The hacker also compromised multi-tenant applications to move across tenants, access additional resources within the tenants, and exfiltrate data. If the compromised application had privileges to interact with the Exchange Web Services (EWS) API, the threat actors were seen compromising email data via EWS.
Related: Rapid7 Connects PostgreSQL Zero-Day to BeyondTrust Exploitation
Related: CISA Warns of Second BeyondTrust Vulnerability Exploited in Attacks
Related: China Targeted Foreign Investment, Sanctions Offices in US Treasury Hack
Related: CISA Urges Immediate Patching of Exploited BeyondTrust Vulnerability