Swiss data protection firm Acronis has clarified that a single customer’s account has been compromised after a hacker leaked gigabytes of information allegedly stolen from the company.
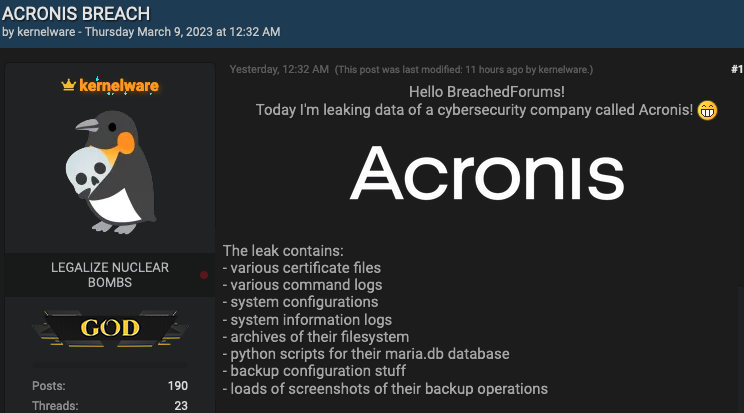
A hacker announced on a popular cybercrime forum on Thursday that they were “leaking data of a cybersecurity company called Acronis”, claiming that they hacked the company because they were bored and wanted to humiliate them.
The hacker is the same who recently offered to sell 160 Gb of data stolen from computer giant Acer. The company immediately confirmed that one of its document servers had been hacked, but said no customer data was stored on the compromised machine.
In the case of Acronis, the cybercriminal published a 12 Gb archive file allegedly containing certificate files, command logs, system configurations and information logs, filesystem archives, scripts, and backup configuration data.

Acronis offers backup, disaster recovery, antivirus, and endpoint protection management solutions. After the incident came to light, the company’s CISO, Kevin Reed, clarified in a post on LinkedIn that the leaked data appears to come entirely from a single customer’s account.
“Based on our investigation so far, the credentials used by a single specific customer to upload diagnostic data to Acronis support have been compromised. We are working with that customer and have suspended account access as we resolve the issue. We also shared IOCs with our industry partners and work with law enforcement,” Reed said.
He added, “No other system or credential has been affected. There is no evidence of any other successful attack, nor there is any data in the leak that is not in the folder of that one customer. Our security team is obviously on high alert and the investigation continues.”
Acronis has also separately clarified that none of its products are impacted by the breach.
Related: 25k Nissan Customers Affected by Data Breach at Third-Party Software Developer
Related: Atlassian Investigating Security Breach After Hackers Leak Data
Related: 20 Million Users Impacted by Data Breach at Instant Checkmate, TruthFinder