Japanese e-commerce and logistics company Askul has revealed that a recent data breach stemming from a ransomware attack has resulted in over 700,000 records being compromised.
Askul, which specializes in B2B sales of office and professional supplies, detected the attack on October 19, after cybercriminals started encrypting files on its systems.
However, prior to the data encryption being initiated, the hackers stole sensitive information from the company’s systems in an effort to increase their chances of getting paid.
The RansomHouse ransomware group took credit for the attack on Askul in late October, leaking data allegedly stolen from its systems on November 10 and December 2. The fact that data has been made public indicates that the company has refused to pay a ransom.

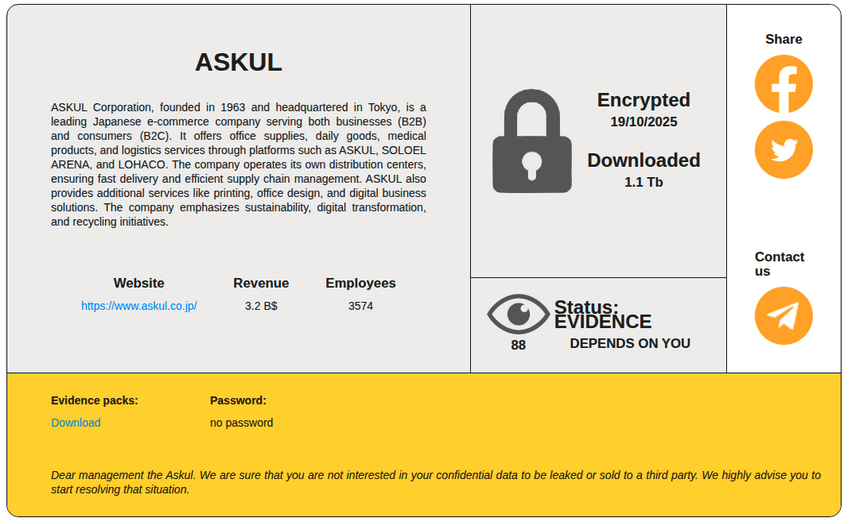
The cybercriminals claimed to have stolen more than 1 TB of data from the company.
According to Askul, the cyberattack has resulted in significant disruptions, including to orders and shipping. The company said its logistics systems, which are highly automated, were also shut down.
It took the company until early December to start resuming many of the impacted services.
The company admitted that the data breach impacted customer and business partner information.
Specifically, roughly 590,000 customer records related to business services and 132,000 records related to consumer services have been compromised. In addition, the hackers stole thousands of records related to business partners, employees, and Askul executives.
The company’s investigation showed that the cybercriminals gained access to its network using compromised credentials. After obtaining initial access to Askul systems, the attackers conducted reconnaissance, harvested credentials, moved laterally, and disabled security systems. File-encrypting malware was deployed after backup files were deleted, the company said in an incident report written in Japanese.
Askul is not the only major Japanese company to have been targeted by cybercriminals in recent months. The list also includes beer giant Asahi, media company Nikkei, and a Nippon Steel subsidiary.
Related: Japan Airlines Was Hit by a Cyberattack, Delaying Flights During the Year-End Holiday Season
Related: Japan’s Space Agency Was Hit by Multiple Cyberattacks, but Officials Say No Sensitive Data Was Taken