Law enforcement agencies in four countries, working with Europol and private partners, have disrupted SocGholish infrastructure and cleaned up nearly 15,000 infected WordPress websites.
Active since 2017 and also known as FakeUpdates, SocGholish is a malware framework injected into websites running popular content management systems, such as WordPress, Joomla, and Drupal, either via known vulnerabilities or stolen credentials.
The framework acts as a JavaScript-based dropper, deploying various malware families as part of drive-by downloads, including ransomware, banking trojans, spyware, and more, and has been one of the most used loaders for years.
SocGholish is operated by a Russian-speaking threat actor tracked as DEV-0206, Gold Prelude, Mustard Tempest, TA569, and UNC1543, which acts as an initial access broker and has been associated with the infamous Evil Corp gang (believed to be linked to Russian intelligence).
TA569 has been observed indiscriminately compromising websites to inject the SocGholish loader, including prominent media and retail portals visited by millions of users daily.
The malware profiles a victim’s browser, performs specific checks, and then overwrites the entire webpage with a fake browser update to entice the user into downloading a malicious payload, Proofpoint explains.
Orange’s cyber defense unit observed SocGholish delivering loaders like Gholoader and MintsLoader, which eventually led to payloads such as the GhostWeaver PowerShell backdoor, LockBit and RansomHub ransomware, and AsyncRAT or NetSupport RAT backdoors.
According to Infoblox, approximately 55% of cloud customers were exposed to SocGholish this year, which demonstrates the high risk the botnet poses to enterprises worldwide.
The ShadowServer Foundation puts that into better perspective: in May, there were more than 1.44 million compromised WordPress websites available for use by SocGholish.
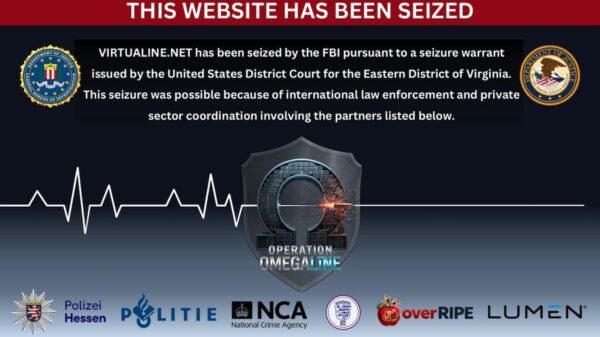
Authorities in the Netherlands, Canada, the US, and Germany, with support from Europol, took down 106 command-and-control (C&C) servers and domains associated with SocGholish, and removed backdoors and malware from 14.971 infected WordPress websites.
The Dutch police say notifications were also sent to WordPress site owners whose compromised credentials were identified, urging them to change their logins, enable MFA, delete suspect accounts, and keep their sites updated.
Related: Dutch Police Dismantle Massive 17-Million-Device Botnet
Related: GlassWorm Botnet Disrupted
Related: Tycoon 2FA Fully Operational Despite Law Enforcement Takedown
Related: SystemBC Infects 10,000 Devices After Defying Law Enforcement Takedown