
Connect with us

Hi, what are you looking for?

SecurityWeekSecurityWeek

Vulnerabilities

Siemens Patches Authentication Bypass Bug in Telecontrol Product

Siemens has released a firmware update for SICAM MIC devices in order to patch a serious vulnerability reported to the company by an external researcher.

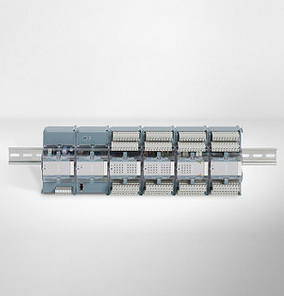
Siemens SICAM MIC, which is part of the SICAM RTU product family, is a modular telecontrol device designed for energy automation. The product is deployed worldwide in the energy and other sectors.
Siemens has released a firmware update for SICAM MIC devices in order to patch a serious vulnerability reported to the company by an external researcher.

Siemens SICAM MIC, which is part of the SICAM RTU product family, is a modular telecontrol device designed for energy automation. The product is deployed worldwide in the energy and other sectors.

Siemens SICAM MIC

According to advisories published by Siemens and ICS-CERT, SICAM MIC devices are plagued by an authentication bypass vulnerability (CVE-2015-5386) that can be exploited remotely by an attacker with medium skill.

“Attackers with network access to the device’s web interface (port 80/tcp) could possibly circumvent authentication and perform administrative operations,” reads Siemens’ description of the vulnerability.

The bug was identified and reported to Siemens by Philippe Oechslin, founder of Swiss IT security consulting company Objectif Sécurité.

The flaw is considered a high severity issue (CVSS v2 base score of 8.3), but Siemens has pointed out that for the attack to work the attacker needs to have network access to the device’s web interface, and a legitimate user must be logged in to interface.

Advertisement. Scroll to continue reading.

The security hole affects Siemens SICAM MIC devices running versions of the firmware prior to V2404. With the release of version V2404, Siemens has patched the authentication bypass issues and it has introduced further security improvements. The company advises customers to install the latest firmware update.

“As a general security measure Siemens strongly recommends to keep the firmware up-to-date and to protect network access to the SICAM MIC with appropriate mechanisms. It is advised to configure the environment according to our operational guidelines in order to run the devices in a protected IT environment,” Siemens said in its advisory.

Related: Learn more at the ICS Cyber Security Conference

Related: Siemens Patches DoS, Other Vulnerabilities in SIMATIC HMI Products

Written By

Eduard Kovacs (@EduardKovacs) is senior managing editor at SecurityWeek. He worked as a high school IT teacher before starting a career in journalism in 2011. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing for the latest cybersecurity threats, trends, and expert insights.

Click to comment

Trending

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

Learn how to address potential risks and not restrict AI adoption in your organization. See what a centralized AI gateway is and how it works in practice.

Register

Join as we decipher the world of zero trust and share war stories on securing an organization by eliminating implicit trust and continuously validating every stage of a digital interaction.

Register

People on the Move

Lumen Technologies has named Kim Keever as CSO.

Quantum Secure Encryption Corp. has appointed Joseph Hall as CIO.

David Cass has joined Grayscale Investments as Chief Risk Officer.

More People On The Move

Expert Insights

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest cybersecurity news, threats, and expert insights. Unsubscribe at any time.





