
Researchers have demonstrated that the Cisco ASA exploit leaked recently by a group called Shadow Brokers can be leveraged for remote code execution against newer versions of the software as well.
Shadow Brokers has released roughly 300Mb of firewall exploits, implants and tools allegedly stolen from the NSA-linked Equation Group. Security firms and documents leaked by whistleblower Edward Snowden have shown that the code is genuine, but experts noted that the most recent files date back to 2013.
The exploits, implants and tools target products from Cisco, Fortinet, WatchGuard, Juniper Networks and other vendors. Each of these companies has analyzed the leaked code, but so far only Cisco identified a previously unknown vulnerability (CVE-2016-6366).
The flaw, affecting the Simple Network Management Protocol (SNMP) code of Cisco Adaptive Security Appliance (ASA) software, can be exploited by a remote attacker who has access to the targeted system to execute arbitrary code and obtain full control of the device. Cisco has yet to release a patch for the security hole, but it has provided some workarounds.
The leaked exploit for CVE-2016-6366, dubbed “EXTRABACON,” is several years old so it only works properly on older ASA versions. However, researchers from Hungary-based security firm Silent Signal managed to modify the leaked exploit for ASA 9.2(4), a version released in July 2015.
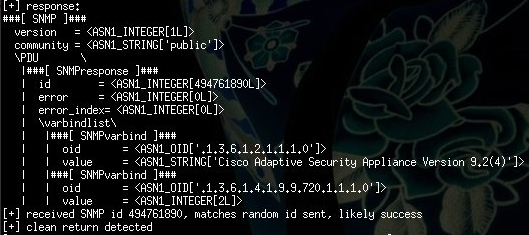
Moreover, Balint Varga-Perke, IT security expert and co-founder of Silent Signal, told SecurityWeek that the exploit can likely be adapted for even newer versions. The security firm is currently working on automatically generating exploit code for Cisco ASA versions that are currently not supported. Adapting the exploit for ASA 9.2(4) only took Silent Signal researchers a few hours.
“Unfortunately, some only realize the risk of a vulnerability if there is a practical demonstration of it,” Varga-Perke said in an email. “We hope that this development clarifies the risk for the skeptics too.”
According to Cisco’s security advisory for CVE-2016-6366, the vulnerability affects all ASA software releases and all supported versions of SNMP. When the vendor tested the leaked exploit against a Cisco ASA 5506 device running version 9.4(1), the software crashed.
However, Omar Santos of the Cisco Product Security Incident Response Team has confirmed that the exploit code can be modified to work against any ASA code.
It’s still unclear who is behind the Shadow Brokers leak. While some suspect that it’s the work of Russia, others believe an NSA insider could be responsible.
Related: Snowden Documents Show NSA Leak is Real
Related: Firewall Vendors Analyze Exploits Leaked by “Shadow Brokers”






