
Keeper Security has filed a lawsuit against Ars Technica and reporter Dan Goodin over an article covering a serious vulnerability found by a Google researcher in the company’s password manager.
Google Project Zero researcher Tavis Ormandy revealed last week that he had identified a critical vulnerability in the browser extension for the Keeper password manager.
The flaw, very similar to one discovered by the expert just over one year ago in the same application, could have been exploited by hackers to steal passwords stored by the extension if they could convince an authenticated user to access a malicious website.
Keeper Security released a patch within 24 hours of the flaw being reported and there had been no evidence of exploitation in the wild. The vendor highlighted that the security hole only impacted the browser extension and not the Keeper desktop application.
These types of vulnerabilities are often covered by the media, particularly ones found by Ormandy, who is known for discovering critical, easy-to-exploit weaknesses in popular software. However, Keeper Security does not like the article written by Ars Technica Security Editor Dan Goodin on this story and filed a lawsuit against him and his employer.
Goodin’s initial article, titled “Microsoft is forcing users to install a critically flawed password manager,” claimed the application had a 16-month-old bug, but it was later updated after Keeper clarified that only a version released this month had been impacted. Despite at least two other updates made to the story, Keeper is still not happy with it and has filed a lawsuit in an effort to get the article removed.
It its complaint, Keeper claims the article “was intended to and did cause harm” to the company by making “false and misleading statements.” The suit covers three counts: defamation, violation of the Uniform Deceptive Trade Practices Act, and commercial disparagement.
Keeper, which requested a jury trial, wants Ars and Goodin not only to remove the story, but also to be awarded damages and have legal costs covered.
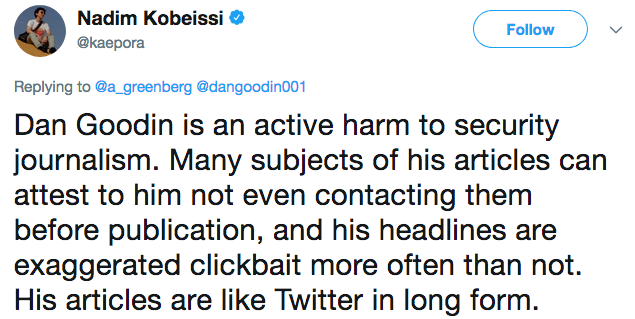
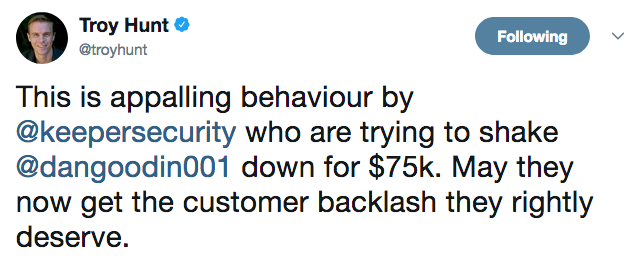
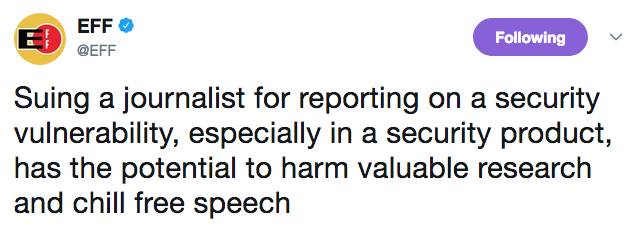
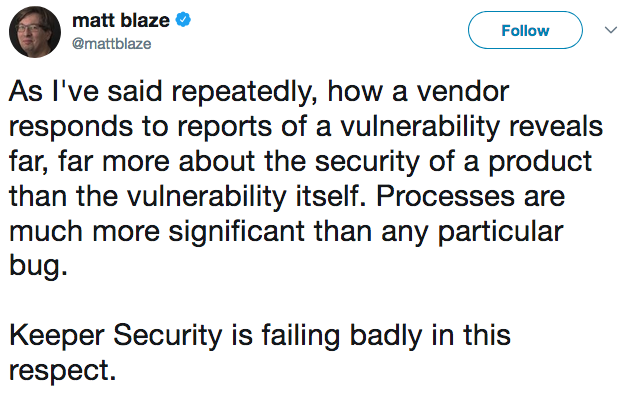
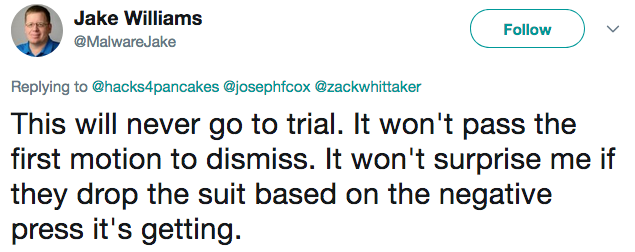
While some members of the cybersecurity industry have taken Keeper Security’s side, saying that many of Goodin’s stories are sensationalized, most have sided with the reporter and believe the lawsuit will cause more damage to the company than the article. Several people believe it will have a so-called “Streisand effect.”
This is not the first time Keeper Security has resorted to legal action over vulnerability disclosures. Back in 2013, it threatened to sue Netherlands-based security firm Fox-IT after it had discovered a critical flaw in one of its products.







You must be logged in to post a comment Login