
Connect with us

Hi, what are you looking for?

SecurityWeekSecurityWeek

ICS/OT

Hardcoded Credentials Give Attackers Full Access to Moxa APs

Taiwan-based industrial networking, computing and automation solutions provider Moxa has released an update for some of its wireless access points (APs) to address a critical vulnerability that can be exploited by hackers to gain complete control of affected devices.

Taiwan-based industrial networking, computing and automation solutions provider Moxa has released an update for some of its wireless access points (APs) to address a critical vulnerability that can be exploited by hackers to gain complete control of affected devices.

Researchers at Cisco’s Talos intelligence and research group have analyzed Moxa’s AWK-3131A AP/bridge/client product, which is recommended for any type of industrial wireless application, and discovered hardcoded credentials corresponding to an account that cannot be disabled or removed.
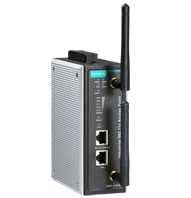
Moxa AP

According to researchers, an attacker can leverage the username “94jo3dkru4” and the password “moxaiwroot” to log in to an undocumented account that provides root privileges.

The flaw, tracked as CVE-2016-8717, has been patched by Moxa with a software update. Users who cannot immediately apply the patch have been advised by Cisco to disable remote access services such as SSH and Telnet.

Experts at Cisco have identified a significant number of vulnerabilities as part of their research into Moxa’s AWK-3131A product. The list includes authentication issues that allow dictionary attacks and session hijacking, many cross-site scripting (XSS) vulnerabilities in the web interface, information disclosure bugs, denial-of-service (DoS) flaws, and several command injections.

Learn More at SecurityWeek’s 2017 Singapore ICS Cyber Security Conference

Advertisement. Scroll to continue reading.

Technical details on the other security holes were made public earlier this month after Moxa had released fixes. CVE-2016-8717 was mentioned in Cisco’s initial advisory, but its details were not disclosed to prevent potential attacks.

Cisco said Moxa has been very cooperative and it even gave researchers access to some of its source code.

Related: Flaws Found in Moxa Industrial Ethernet Products

Related: Flaws Allow Remote Hacking of Moxa MiiNePort Devices

Related: Eight Vulnerabilities Found in Moxa NPort Devices

Related: Flaws Found in Moxa Factory Automation Products

Written By

Eduard Kovacs (@EduardKovacs) is senior managing editor at SecurityWeek. He worked as a high school IT teacher before starting a career in journalism in 2011. Eduard holds a bachelor’s degree in industrial informatics and a master’s degree in computer techniques applied in electrical engineering.

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing for the latest cybersecurity threats, trends, and expert insights.

Click to comment

You must be logged in to post a comment Login

Leave a Reply

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest threats, trends, and technology, along with insightful columns from industry experts.

NOW LIVE: CISO Forum 2026 Summit

Join as we bring together CISOs, senior cybersecurity executives, practitioners, industry experts, and other security leaders to share practical experience and examine the issues shaping enterprise cybersecurity strategy.

Register

Join to learn the four levels of architecting security into the agentic SDLC – from securing the code your developers' agents write to running a coordinated system of security agents you've built yourself.

Register

People on the Move

Kirsten Davies has been appointed National Cyber Director.

Zifino has appointed Toney E. Jennings as CRO.

Zeke Maldonado has been named Principal Deputy CIO at the US Department of Commerce.

More People On The Move

Expert Insights

Daily Briefing Newsletter

Subscribe to the SecurityWeek Email Briefing to stay informed on the latest cybersecurity news, threats, and expert insights. Unsubscribe at any time.





