The US Justice Department announced on Friday that the Warzone RAT cybercrime enterprise has been dismantled as a result of an international law enforcement operation.
US authorities have also unsealed charges brought against two individuals allegedly selling the malware and offering support to users.
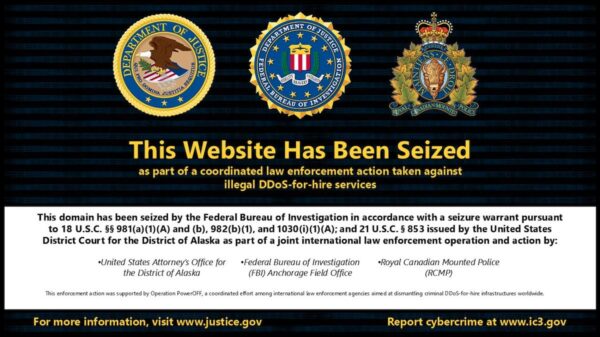
On the technical side, authorities have seized four internet domains that were used to sell the Warzone RAT. The domains now display a takedown notice informing visitors that the websites have been seized as a result of a law enforcement action involving agencies in the US, Canada, Netherlands, Germany, Croatia, Malta, Romania, Finland, Australia, and Nigeria, with support from Europol.
Servers hosting Warzone RAT infrastructure have also been targeted in the law enforcement operation.
Warzone is a remote access trojan that allows users to stealthily connect to infected devices and conduct various activities, such as browsing files, recording keystrokes, taking screenshots, stealing credentials, and spying through the computer’s camera. The cost of a Warzone RAT license ranged between $16 and $38 per month.
The malware is also known as Ave Maria RAT and it has been spotted in numerous attacks, including ones linked to suspected state-sponsored threat actors.
One of the individuals charged for his role in the Warzone RAT operation is 27-year-old Daniel Meli of Malta. He has been charged with causing unauthorized damage to protected computers, illegally selling and advertising an electronic interception device, and participating in a conspiracy to commit computer intrusions.
Authorities said Meli has been selling malware and associated services on cybercrime forums since at least 2012. In addition to Warzone RAT, he is said to have sold Pegasus RAT, and allegedly offered online support to customers of both pieces of malware.
The second suspect is 31-year-old Prince Onyeoziri Odinakachi of Nigeria, who has been charged with obtaining authorized access to protected computers to obtain information, and causing unauthorized damage to protected computers.
Investigators believe Odinakachi provided online support to Warzone RAT customers between at least June 2019 and March 2023.
Both Odinakachi and Meli were arrested on February 7 in their home countries and the US is seeking their extradition. If convicted, they can spend up to 10 years in prison and be ordered to pay a significant fine.
The Justice Department also announced a dedicated website where victims of the Warzone RAT can file a report with the FBI.
Related: US Says 19 People Charged Following 2019 Takedown of xDedic Cybercrime Marketplace
Related: Law Enforcement Reportedly Behind Takedown of BlackCat/Alphv Ransomware Website
Related: US Announces IPStorm Botnet Takedown and Its Creator’s Guilty Plea