Just days after shipping a major security update to correct vulnerabilities in its Aria Operations for Networks product line, VMWare is warning that exploit code has been published online.
In an updated advisory, the virtualization technology giant confirmed the public release of exploit code that provides a roadmap for hackers to bypass SSH authentication and gain access to the Aria Operations for Networks command line interface.
The exploit code and root-cause analysis, released by SinSinology researcher Sina Kheirkhah, documents the problem as a case where VMWare “forgot to regenerate” SSH keys.
He pointed to VMWare’s CVE-2023-34039 advisory (CVSS severity score of 9.8 out of 10) that describes the bug as a network authentication bypass and warns that the issue is being mischaracterized.
“Interestingly, VMware has named this issue “Networks Authentication Bypass”, but in my opinion, nothing is getting bypassed. There is SSH authentication in place; however, VMware forgot to regenerate the keys,” Kheirkha said.
“After reading both descriptions, I realized that this must be a hardcoded SSH key issue,” he said, noting that VMware’s Aria Operations for Networks had hardcoded its keys from version 6.0 to 6.10.
“The main challenge in exploiting this vulnerability is that each version of VMware’s Aria Operations for Networks has a unique SSH key. To create a fully functional exploit, I had to collect all the keys from different versions of this product,” he said.
The release of exploit code for this flaw amplifies the urgency for network admins to apply the available patches from VMWare.
The VMware Aria Operations for Networks product, formerly vRealize Network Insight, is used by businesses to monitor, discover and analyze networks and applications to build secure network infrastructure across clouds.
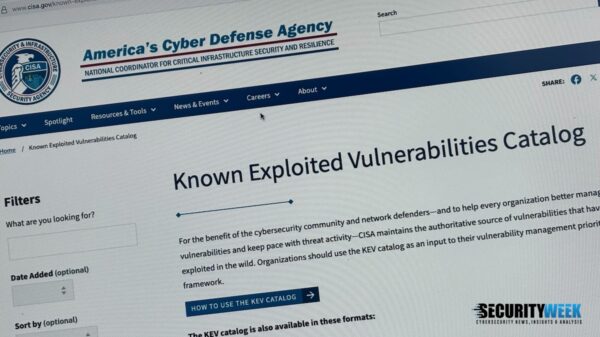
VMware has struggled with security problems in the Aria Operations for Networks product, recently patching a gaping command injection flaw that was remotely exploited in the wild. The Aria Operations for Network product has also been tagged in the U.S. government’s CISA Known Exploited Vulnerabilities catalog.
Related: VMware Confirms Exploits Hitting Just-Patched Security Bug
Related: CISA Tells Agencies to Patch Roundcube, VMware Flaws
Related: VMware Plugs Critical Holes in Network Monitoring Tool
Related: Exploit Published for Major Flaw in VMware Logging Software